Review a request finding
Read a request observation, check the address source and response evidence, then decide what needs further investigation.
For Free 1.2.7 and Pro 1.2.7. Check the download page for available versions and requirements. Verify representative workflows on staging before use.
On this page
You will distinguish the recorded request pattern from its source attribution and any observed response effect.
Logged.ai → Requests → Findings; Source and verification
Available in Free and Pro. Use an account authorized to view request evidence. Changing the address-source configuration requires settings access and knowledge of the site’s proxy boundary; reviewing a finding does not require changing it.
The public demo contains dated fictional observations and is read-only. On your own site, start from an observation the plugin has actually retained.
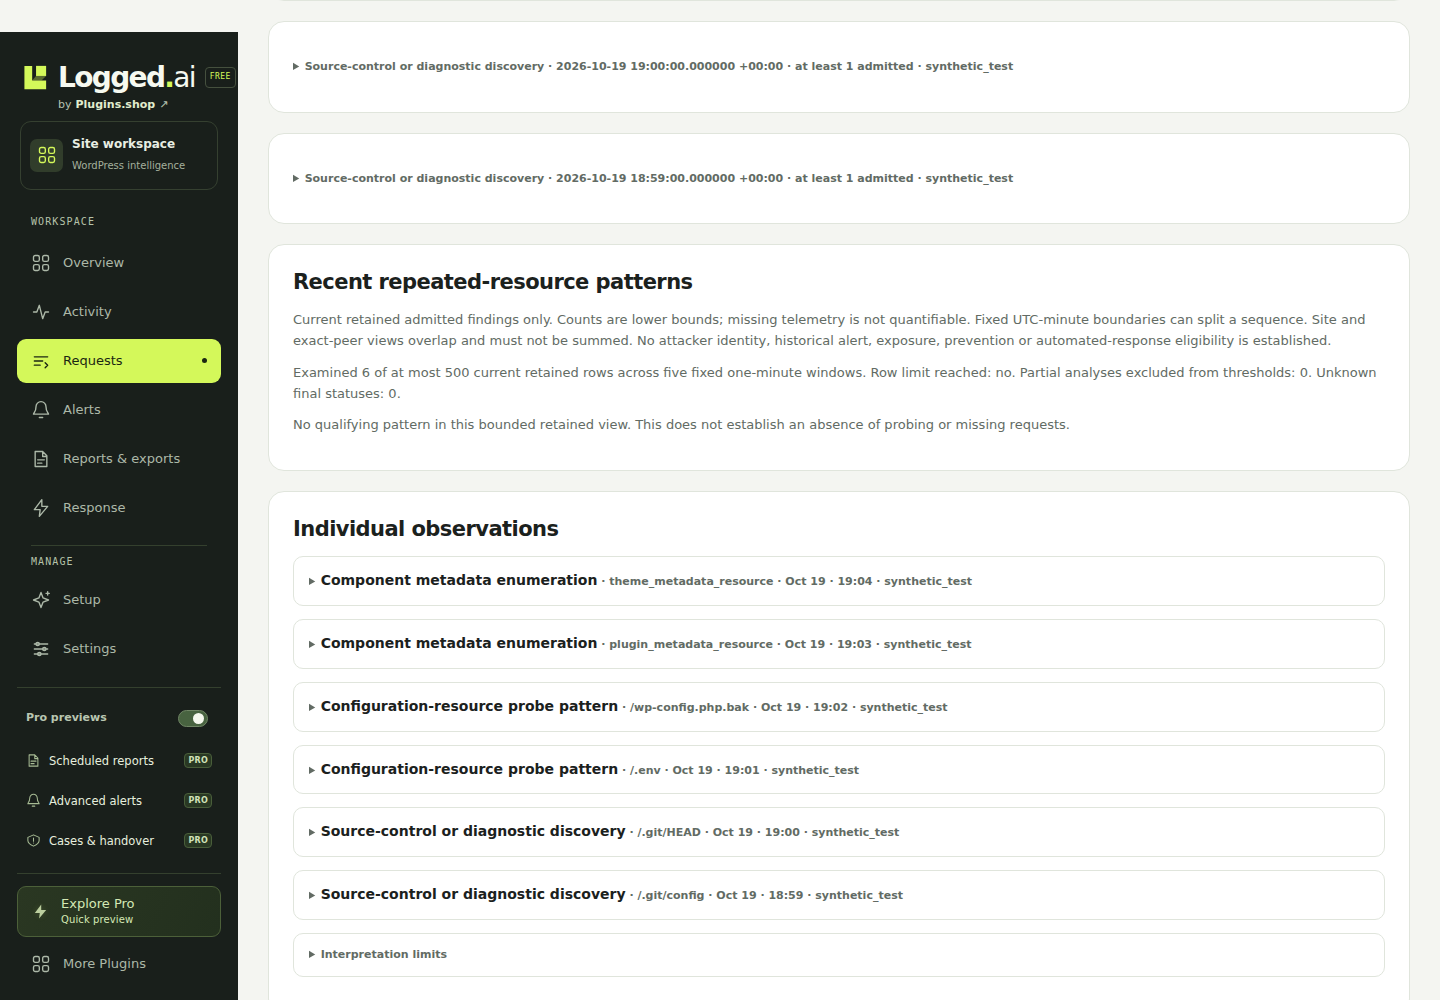
These synthetic observations illustrate the review screen. The counts do not describe every request, identify a person or establish a successful attack.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Synthetic diagnostic observations, not real attacks.Explore this screen in the demo- Open Requests → Findings. Narrow the results with the available request filters, then select a retained observation or minute group.
- Read the pattern, method and minimized path together. A pattern is a reason to review the request; it is not proof of a successful attack.
- Check source quality and the recorded response effect. Keep an observed request, a response decision and the resulting effect separate in your notes.
- Open Source and verification to see how the address was derived. If collection is in doubt, run the harmless Observer self-test on your own installation and inspect its result.
Fictional review
A retained GET observation contains a concerning path pattern. First check the source quality and response effect. If the record does not establish a denial or a successful action, write “pattern observed; effect not established.” Review nearby activity or server/security-plugin evidence before concluding that the site was compromised or that a particular component blocked it.
Actual connection peer is the default address source. Behind a proxy, that peer may be the proxy itself. The alternative is Explicit trusted proxies and X-Forwarded-For, configured with reviewed proxy addresses or CIDRs.
- Ask the server administrator which immediate peers are controlled and trusted for this site. Do not infer that list from an arbitrary incoming header.
- Only after reviewing the boundary, enter the intended trust set and choose Save request-source configuration.
- Recheck a known request and the source-quality result. Changing the source configuration invalidates dependent exact-source targets.
Forwarding is considered only when the immediate peer matches the trust set. Other forwarding headers are ignored. Even a correctly derived or masked address is network context, not a person’s identity.
Interpret observation-only matches
An observation-only response policy can record admitted matching GET/HEAD requests while the response switch is off or on. It does not deny a request or enable an alert. With response enabled, active matching policies take priority. Expiry, exclusions, privacy and admission limits still apply, so these records are not a complete traffic count.
Accepted proxy ranges
Use reviewed exact IPv4 or IPv6 addresses, IPv4 CIDRs from /8 through /32, or IPv6 CIDRs from /16 through /128. IPv4-mapped IPv6 input follows the IPv4 limit. Public CDN ranges are allowed when they describe your actual trusted peers; broad ranges are not a substitute for discovering that boundary. The list is limited to 32 entries.
If an older configuration contains a range outside those bounds, it cannot authorize forwarded-address attribution. Deliberately select direct-peer mode to recover a known source, then save the verified narrower proxy ranges. Do not assume that a forwarded address identifies one person.
The observer sees requests that reach the WordPress plugin layer. Static files, cache hits and responses produced earlier may not reach it. Admitted observations are not a count of all traffic or unique attackers.
A successful self-test covers its one routed request. It does not verify every route, prove that an upstream firewall works, or identify whichever external component blocked an unrelated request.
- Ordinary or explained activity: keep the interpretation proportionate to the evidence.
- Unexpected activity with a related change: inspect the activity record; Pro can organize related evidence in a case.
- A narrowly defined temporary response is justified: follow the preview and recovery guide before enabling a policy.
The self-test or a result is missing
Review the reported diagnostic and System status, then check whether the route reached WordPress at all. Give support the affected route category, time and failure code; avoid sending raw query strings, credentials or unnecessary visitor data.
This guide covers Logged.ai Free 1.2.7 and Pro 1.2.7. Check available versions and package requirements, and verify representative workflows on staging before updating your main site.
Get help with your next step.