17 practical chapters and a plain-language glossary for Free 1.2.7 and Pro 1.2.7. Read a task online, download the complete PDF, or print this manual. Check which versions are available before updating.
Install Free, add the compatible Pro ZIP if needed, and verify that the workspace is ready before using it on your main site.
By the end of this guide
You will have Free running on its own, or a compatible Free and Pro pair, with the first setup and health checks completed.
Where to start
WordPress → Plugins → Add New Plugin → Upload Plugin
Before you start
Use a WordPress account allowed to install and activate plugins. On multisite, ask the network administrator to confirm the installation and site scope first.
Host: WordPress 6.7 or later, PHP 8.0 or later, and MySQL or MariaDB with the standard WordPress database connection. SQLite and WordPress Playground are not supported.
Packages: this guide covers Free 1.2.7 and Pro 1.2.7. Pro 1.2.7 requires Free 1.2.7 or later with edition API 2. Check available downloads before starting; a prepared release is not necessarily available through WordPress or your account yet.
Recovery: a current site backup and a staging installation where you can check the result.
If your delivery is an outer bundle containing two ZIPs, extract that bundle on your computer. Upload each plugin ZIP separately; WordPress cannot install the outer bundle as a plugin.
Install Free, then add Pro
In Plugins → Add New Plugin → Upload Plugin, choose the Free ZIP, select Install Now, then activate Logged.ai.
For Pro, repeat the upload with the compatible Pro ZIP and activate it. Keep Free active. Then open Logged.ai → Licence & updates and activate your licence for this site to unlock new Pro work.
Open Logged.ai → Setup and follow the first workspace setup. A local workspace does not require an external AI account.
Open Settings → System status. Read any requirement, storage, collection or scheduling message before continuing.
Updating to 1.2.7: first confirm that the release is available from the download page and your account. Back up and test the compatible pair on staging. In WordPress, choose Plugins → Add New Plugin → Upload Plugin → Replace current with uploaded. Replace Free first, then Pro in a separate upload; keep Free active and do not uninstall either plugin. Free-only sites replace only Free. An update offer is separate from a successful installation and must pass the usual compatibility, entitlement and archive checks.
Check the result
The WordPress Plugins screen shows Free active and, if installed, the compatible Pro add-on active. For this release, verify Free 1.2.7 and Pro 1.2.7; for a later release, follow its stated dependency requirements.
Logged.ai opens for your authorized account, and the setup choices are reflected in the workspace.
System status does not leave an unexplained requirement or failed upgrade state.
Open a retained activity record, or make a small, reversible content change on staging and check its recorded outcome. Logging cannot reconstruct changes from before collection was active.
A newly installed workspace can legitimately be quiet. The useful check is whether an expected, supported new action is recorded—not whether the dashboard is already full.
If installation stops
WordPress says the package is invalid
Check that you selected the inner Free or Pro plugin ZIP, not the outer delivery bundle. Download a fresh copy from Downloads (Release notes) or your account if the archive was incomplete.
Activation reports a dependency or server requirement
Confirm Free is active before Pro and compare both versions. For a database or PHP requirement, give the exact message to your host; do not bypass the activation check. On PHP 8.0 or 8.1, a message about exception arguments means the host must enable zend.exception_ignore_args so secrets stay out of exception logs.
I can install plugins but cannot open an evidence screen
Installation access and Logged.ai evidence permissions are separate. Use the permission reference to identify the right site and required access.
Optional Pro update connection
You can replace compatible ZIPs manually without configuring the in-plugin updater. New installations still need successful licence activation before starting Pro work. Installations initialized before 0.1.8 retain local access on their current site and environment; paid updates require a valid licence. Follow Activate Pro and manage updates for activation, migration and hosting details.
Chapter 02 · Task guide · Free & Pro
Set up your first workspace
Choose a useful starting view, make a deliberate collection decision, and finish with one real evidence check.
By the end of this guide
You will know which display settings you chose, whether collection changed, and where to check that the workspace is recording useful evidence.
Where to start
Logged.ai → Setup
Before you start
Free supports this guide; Pro adds optional workflows. Use an account with permission to manage Logged.ai settings on the intended WordPress site. Have the existing retention and collection settings in mind before choosing a preset.
If the site already has an agreed collection policy, keep it while you adjust the appearance. You can revisit setup later.
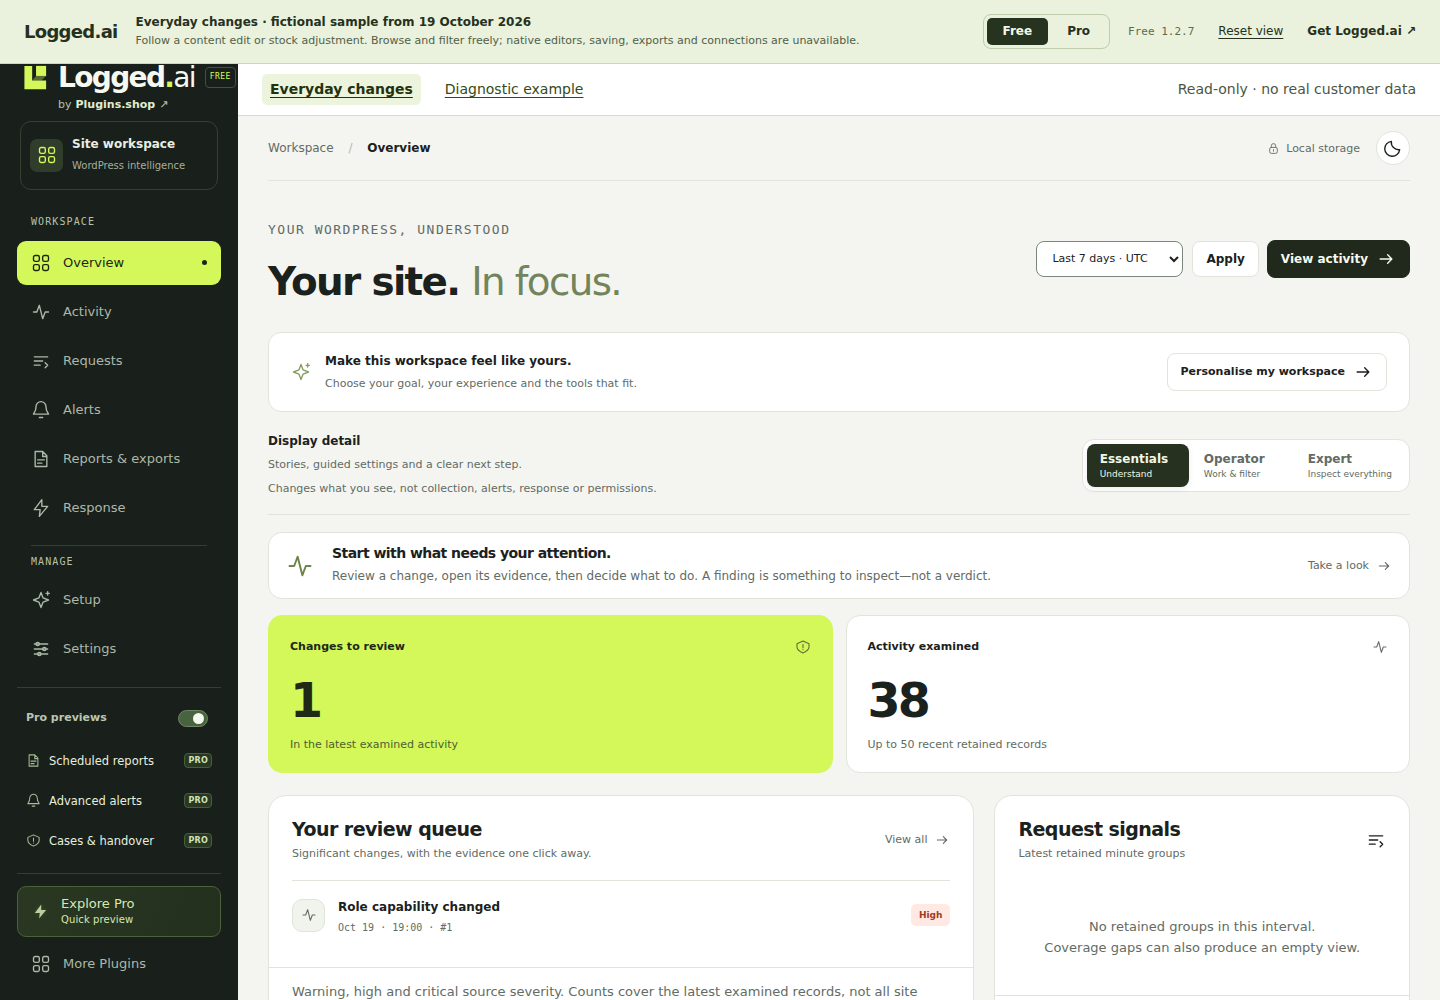
Free Overview after setup
The sidebar opens your workspace areas. Display detail changes presentation; collection, permissions and saved settings remain separate choices.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Follow the four steps
In Your goal, choose your immediate job: understanding activity, reviewing access, troubleshooting changes or reviewing store activity. This personalizes recommendations.
In Your experience, choose Essentials, Operator or Expert, then light or dark appearance. Use the sample to judge how much detail you need.
Review Your toolkit. Suggested workflows do not purchase Pro or connect a remote service.
At Review & launch, choose Keep current settings unless you deliberately want the suggested collection preset. If you do, read the category and retention changes before confirming.
If retention becomes shorter, review the separate deletion confirmation. Then choose Finish setup and Open my workspace.
Without JavaScript
All four steps remain visible. Choose the options and use Finish setup; review the existing preset details and required confirmations before applying a preset.
What setup changes
Goal, display detail and appearance shape the interface. Applying a collection preset changes which new events can be collected and may change retention. Those are separate decisions.
A more detailed display does not grant permissions.
Choosing a goal does not enable alerts or active response policies.
Keeping current collection settings leaves that policy in place.
Shorter retention can remove older evidence; increasing it later cannot recover records already removed.
Example: investigate recent content changes
A practical first setup
For a staging site where you are checking unexpected edits, choose the troubleshooting goal and Operator detail. Keep the existing collection settings on the final step. Open Activity and search for content, then inspect a relevant record. This lets you learn the workspace without changing the site’s collection policy.
Check the result
Read the completion summary: your focus, current retention and excluded new-event categories. Confirm it matches your choice.
Open Overview, then Settings → System status for monitoring health. A setup success message is not a security scan.
A confirmation fails or the settings changed while I was reading
Reload the current settings, compare them with your intended choices, and submit again only after reviewing the new state. Do not assume an unsaved draft was applied. See display detail and saving.
Find your tools and control previews
Workspace groups Overview, Activity, Requests, Alerts, Reports & exports and Response. Activated Pro also includes Cases & handover. Manage contains Setup and Settings. The links you see still depend on your permissions and the current site.
In Free, the Pro previews switch hides or restores the three examples: Scheduled reports, Advanced alerts and Cases & handover. The switch stays visible and saves the choice for your administrator account on this site. Explore Pro remains below the group. Settings also provides controls for optional suggestions.
Activated Pro shows Pro toolkit instead of the Free preview group. Opening guidance does not enable alerts, schedules or response rules. More Plugins opens a locally bundled catalogue; it does not install another plugin or request an external catalogue. Visiting a product’s website is a separate link.
Changing the saved preview preference requires JavaScript. Without it, visible preview links open their normal local preview pages. In the public fictional demo, the switch changes only the current demo tab; it does not save an administrator preference.
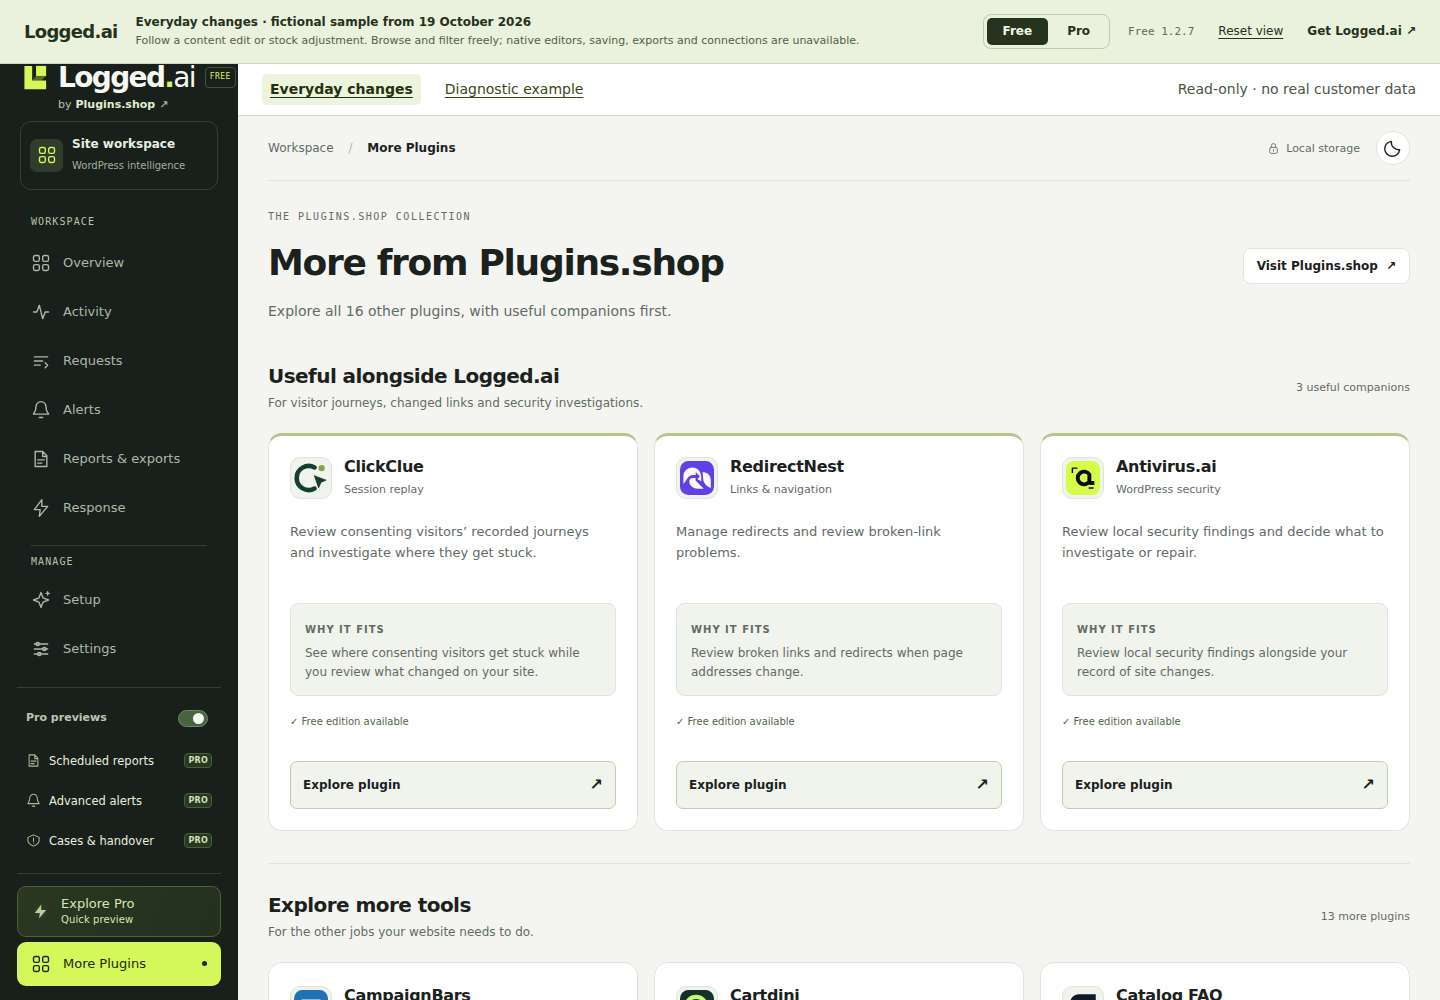
More Plugins, inside your workspace
Browse the publisher’s locally bundled catalogue. Choosing a product website is a separate action; no plugin is installed here.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Chapter 03 · Task guide · Free & Pro
Find who changed what
Answer one concrete question with a filtered activity record, its actor, affected object and recorded outcome.
By the end of this guide
Finish with an evidence reference and a precise description of the recorded change.
Where to start
Logged.ai → Activity → Events
Before you start
Available in Free and Pro. You need permission to view activity on the selected site, and the relevant activity must still be retained. Have an approximate date, action or affected account/object ready.
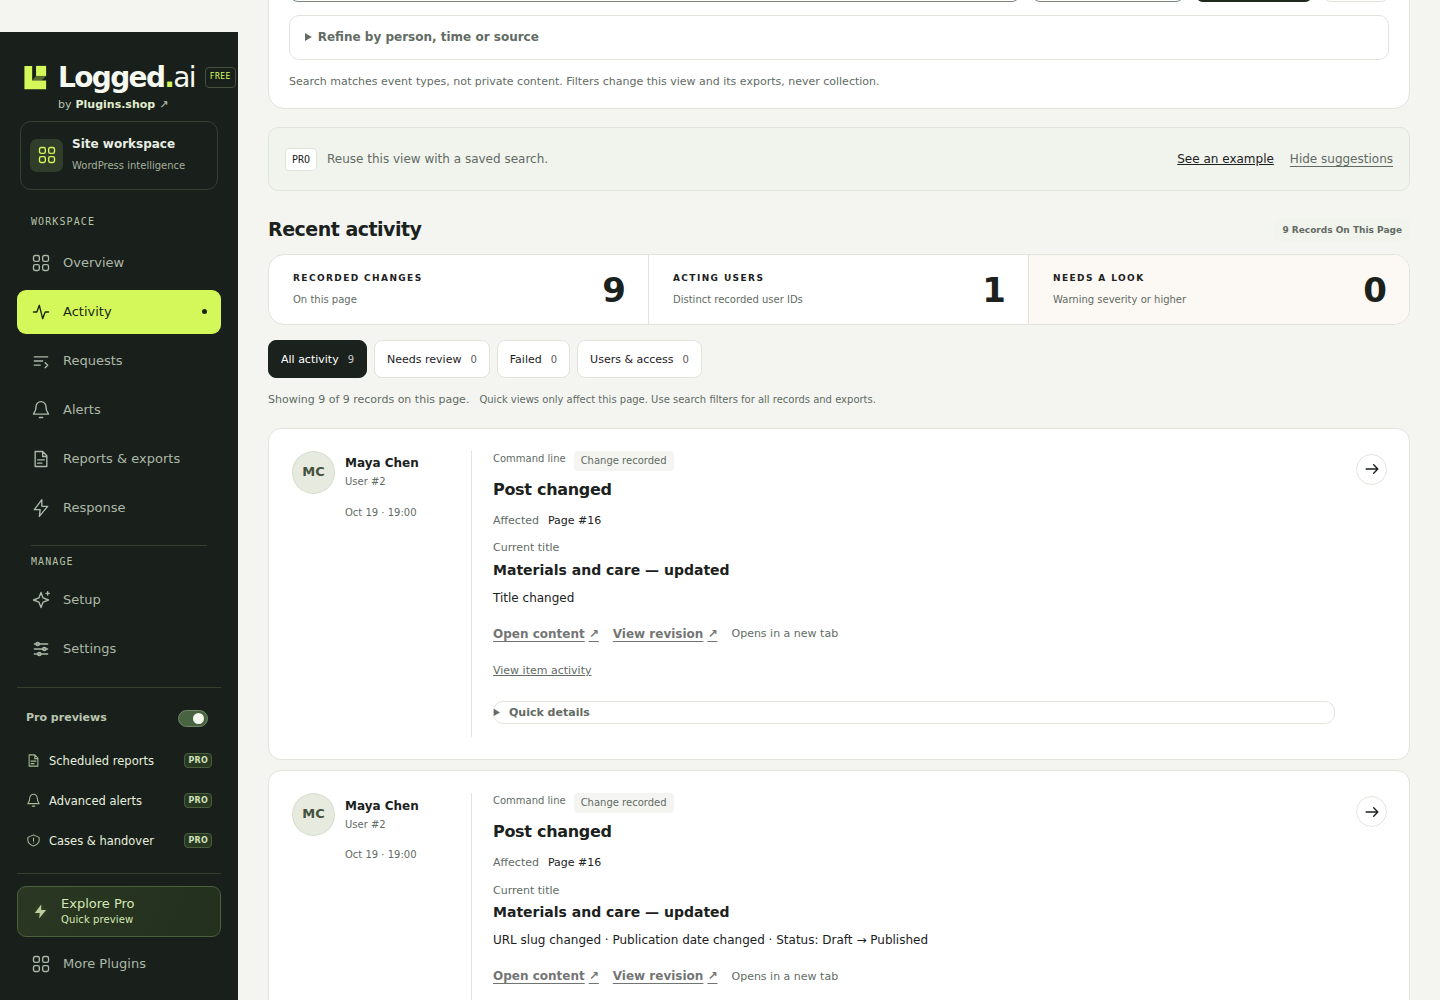
Free Activity: recent recorded changes
Read the acting user, affected object and recorded result separately. Current content labels help navigation; they are separate from retained evidence.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Find the relevant record
Enter an action word in Find a type of change, such as role, plugin or content. Choose In this area if you know the category, then select Find changes.
Open Refine by person, time or source. Use Affected user ID when you know whose account changed; use Acting user ID when you know who performed the operation. Add an object ID, outcome or execution channel only when it helps narrow the question.Where do I find a WordPress user ID?
A user ID is a number, not a username or email address. If your account is already allowed to view and edit that user, open Users → All Users, find the account and choose Edit. Read the number after user_id= in the address bar: user-edit.php?user_id=42 means user ID 42. You do not need to save anything.
Your own Profile page may have no user_id parameter. If the link is unavailable or you need your own ID, ask an authorized administrator to confirm the number. Use the ID from this WordPress installation; the same number on an unrelated installation can refer to someone else. On multisite, also confirm the selected site. Do not broaden permissions just to look up an ID.
Choose a UTC date interval and select Apply filters. The start date is included; the end date is excluded.
Open a relevant record. Read Actor, Affected object, Outcome and Captured field differences. If offered, follow Activity from this request to inspect linked records.
Example: who changed Maya’s role?
Fictional review
Start with role. If Maya is the affected account, enter Maya’s WordPress ID in Affected user ID—not Acting user ID. To cover 19 October 2026 in UTC, use From 2026-10-19 and Until 2026-10-20. Open the record and check who acted, which roles changed and the outcome. If the record names Alex as actor and Maya as affected user, do not describe Maya as having made the change.
Read the evidence carefully
The actor performed the observed operation; the subject is the account or object affected. Current profile labels help navigation but are not a historical profile snapshot. The recorded outcome distinguishes an attempt or failure from a stored change.
Missing before-and-after values do not establish that nothing changed. Unsupported operations, excluded categories and direct database edits can be absent. A shared request identifier adds context; it does not establish why the operation happened.
Search matches up to four terms against recorded action types, not private post content. Filters change the view and its exports; they do not change collection.
Open the content, then follow its history
For a retained supported post, page, product or order event, Open content, Open product or Open order opens its native WordPress/WooCommerce screen in a separate tab when your current permissions allow it. A current title helps you recognize the item; it is not a historical title snapshot. If the exact recorded revision still exists and is accessible, the revision link opens that revision. A deleted, restricted or unavailable item stays unavailable.
Use View activity in supported content and product lists or editors, and in legacy or HPOS order editors, to review that item’s retained events. The shortcuts in native lists and editors require current item access and permission to view Activity. Alongside an authorized Activity record, View item activity filters retained records for that item. Native order-list shortcuts are unchanged. The new tab preserves unsaved work in the editor.
Read recorded commerce changes
Supported price, stock and order changes show compact before-and-after values directly in Activity. These are the values retained with that event, including recorded currencies and any unset, unavailable or redacted side. They are not fetched from today’s product or order. Expand the event to inspect the supporting details; the display does not add evidence to stored records or exports.
Pro: once the filters answer your question, choose Save this Activity view to review them in a private saved-search form. Follow the saved-search guide before adding a schedule.
Recognize a change without retaining its private value
Activity includes clear markers for supported URL-slug, publication-date, comment and pingback-setting changes. Related date fields share one readable summary. These markers say that a field changed; they do not add its raw value or the article text to retained evidence. Untitled content still records a supported change when WordPress supplies its final URL slug.
Supported WooCommerce price, percentage and fractional-stock changes retain their available precision. Native scheduled-sale changes can record the effective price. This does not promise coverage of every commerce extension, custom data store or scheduler.
Check your answer
You can point to a specific event reference and its time.
You have kept the acting user and affected object separate.
Your explanation includes the recorded outcome and any missing evidence.
Choose Reset, confirm the correct WordPress site, and start again with one action word.
Widen the UTC interval and remove person/object filters one at a time. An affected account ID is not always the actor ID.
Check collection, retention and System status. If the event predates collection or was removed, changing the search cannot bring it back. See collection and coverage limits.
Chapter 04 · Task guide · Free & Pro
Review a request finding
Read a request observation, check the address source and response evidence, then decide what needs further investigation.
By the end of this guide
You will distinguish the recorded request pattern from its source attribution and any observed response effect.
Where to start
Logged.ai → Requests → Findings; Source and verification
Before you start
Available in Free and Pro. Use an account authorized to view request evidence. Changing the address-source configuration requires settings access and knowledge of the site’s proxy boundary; reviewing a finding does not require changing it.
The public demo contains dated fictional observations and is read-only. On your own site, start from an observation the plugin has actually retained.
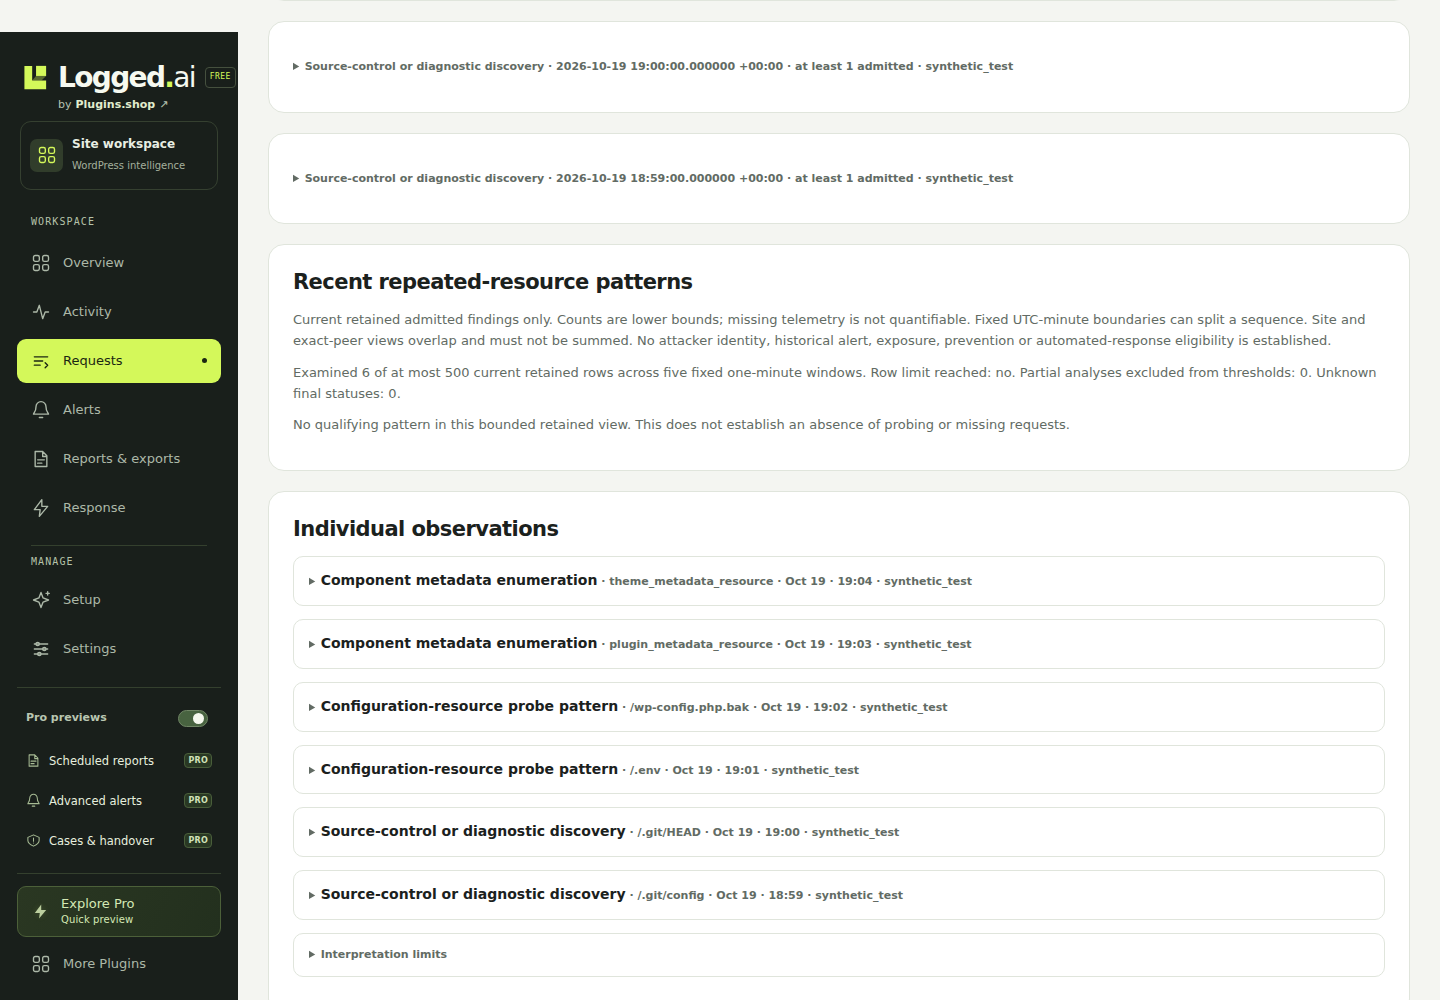
Free Requests: a diagnostic example
These synthetic observations illustrate the review screen. The counts do not describe every request, identify a person or establish a successful attack.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Synthetic diagnostic observations, not real attacks.Explore this screen in the demo ↗
Inspect the observation
Open Requests → Findings. Narrow the results with the available request filters, then select a retained observation or minute group.
Read the pattern, method and minimized path together. A pattern is a reason to review the request; it is not proof of a successful attack.
Check source quality and the recorded response effect. Keep an observed request, a response decision and the resulting effect separate in your notes.
Open Source and verification to see how the address was derived. If collection is in doubt, run the harmless Observer self-test on your own installation and inspect its result.
Example: a suspicious path with no confirmed effect
Fictional review
A retained GET observation contains a concerning path pattern. First check the source quality and response effect. If the record does not establish a denial or a successful action, write “pattern observed; effect not established.” Review nearby activity or server/security-plugin evidence before concluding that the site was compromised or that a particular component blocked it.
Trust forwarding deliberately
Actual connection peer is the default address source. Behind a proxy, that peer may be the proxy itself. The alternative is Explicit trusted proxies and X-Forwarded-For, configured with reviewed proxy addresses or CIDRs.
Ask the server administrator which immediate peers are controlled and trusted for this site. Do not infer that list from an arbitrary incoming header.
Only after reviewing the boundary, enter the intended trust set and choose Save request-source configuration.
Recheck a known request and the source-quality result. Changing the source configuration invalidates dependent exact-source targets.
Forwarding is considered only when the immediate peer matches the trust set. Other forwarding headers are ignored. Even a correctly derived or masked address is network context, not a person’s identity.
Interpret observation-only matches
An observation-only response policy can record admitted matching GET/HEAD requests while the response switch is off or on. It does not deny a request or enable an alert. With response enabled, active matching policies take priority. Expiry, exclusions, privacy and admission limits still apply, so these records are not a complete traffic count.
Accepted proxy ranges
Use reviewed exact IPv4 or IPv6 addresses, IPv4 CIDRs from /8 through /32, or IPv6 CIDRs from /16 through /128. IPv4-mapped IPv6 input follows the IPv4 limit. Public CDN ranges are allowed when they describe your actual trusted peers; broad ranges are not a substitute for discovering that boundary. The list is limited to 32 entries.
If an older configuration contains a range outside those bounds, it cannot authorize forwarded-address attribution. Deliberately select direct-peer mode to recover a known source, then save the verified narrower proxy ranges. Do not assume that a forwarded address identifies one person.
Know the blind spots
The observer sees requests that reach the WordPress plugin layer. Static files, cache hits and responses produced earlier may not reach it. Admitted observations are not a count of all traffic or unique attackers.
A successful self-test covers its one routed request. It does not verify every route, prove that an upstream firewall works, or identify whichever external component blocked an unrelated request.
Choose the next step
Ordinary or explained activity: keep the interpretation proportionate to the evidence.
Unexpected activity with a related change: inspect the activity record; Pro can organize related evidence in a case.
A narrowly defined temporary response is justified: follow the preview and recovery guide before enabling a policy.
The self-test or a result is missing
Review the reported diagnostic and System status, then check whether the route reached WordPress at all. Give support the affected route category, time and failure code; avoid sending raw query strings, credentials or unnecessary visitor data.
Chapter 05 · Task guide · Free & Pro
Preview a temporary response safely
Preview a finite WordPress-layer policy, verify its scope, and keep a clear way to disable it before considering active enforcement.
By the end of this guide
You will be able to explain what the policy can match, when it expires and how to revoke or disable it.
Available in Free and Pro with the relevant request and response permissions. Start from an eligible retained observation on your own site. The public demo allows browsing only; it cannot activate policies.
Have recovery ready first
Keep server-level access and a person who can use it available before activating a response. A WordPress admin session alone is not a recovery plan. Read the recovery steps below before proceeding.
Preview before activation
From the observation, choose Preview temporary policy and a finite duration. If the action is unavailable, read the stated evidence or permission requirement instead of bypassing it.
Read the exact site, path or reviewed-source conditions, eligible GET/HEAD methods, expiry and matcher examples. Inspect any exact-path exceptions.
Keep observation-only while assessing scope. This mode records observation without denying a request. Check ordinary site paths that could share the target conditions.
Only if the scope is justified, choose active mode and acknowledge the effect and recovery procedure. Activation also enables local response for valid existing policies, so review those policies too.
Open Response → Manual policies to confirm the saved mode and policy. Choose Revoke when that policy is no longer needed.
Recover or stop a response
For one policy, use Revoke in Manual policies. To stop local response when the dashboard cannot be used, a server operator can run this from the correct WordPress installation, replacing the example site URL:
Alternatively, the operator can add the following to wp-config.php before WordPress loads:
define('LOGGED_AI_DISABLE_RESPONSE', true);
There is no public recovery URL or bypass cookie. After regaining access, inspect the saved response mode and policies before making further changes.
Expiry and exceptions
Expiry is checked on eligible requests without waiting for cron. An exact-path exception applies only to its selected policy; it neither grants WordPress access nor overrides another policy.
Keep query conditions unambiguous
Query-condition policies respect the host’s PHP query separators and input-variable limit. When those rules make the requested match ambiguous or truncate the necessary input, Logged.ai declines that manual-policy match. Preview the exact intended path and condition on your host before enabling a response; this is not a general request firewall.
Understand the effect before relying on it
This is a temporary WordPress-layer control. Earlier code may already have run, and requests answered upstream may never reach it. It does not replace an upstream firewall. Ambiguous or encoded input can remain observation-only.
Exact-source targeting can affect unrelated users behind the same network and ordinary login, checkout or API reads. A narrow-looking address is not necessarily one person.
Check the saved policy
The saved site, target, mode and expiry match the reviewed preview.
Any exceptions are deliberate and attached to the intended policy.
You have checked existing valid policies before enabling local response.
Ordinary access is still usable and the recovery operator knows how to disable response.
If a preview does not match your intent, leave it unsaved and return to the underlying finding. More uncertain evidence is a reason to investigate, not to broaden a policy.
Chapter 06 · Task guide · Free & Pro
Choose your critical security and failure notices
Choose a small set of important events, authorize the right recipients, and verify the saved settings and delivery state.
Free and Pro notification boundaries
From 1.2.0, ordinary plugin-install notification emails require Pro. Administrator creation or promotion, unsafe registration changes, confirmed administrative email changes, selected security-component deactivation, failed-authentication bursts, admitted request findings and response-suppression/failure notices remain Free. These rules still require explicit configuration; no new messages are enabled automatically. Retained routine rules are paused without the activated add-on. Subscription expiry preserves earned local Pro use under the existing licence terms.
By the end of this guide
You will have an intentional alert configuration and know the difference between a queued notification, mail acceptance and actual receipt.
Where to start
Logged.ai → Alerts → Fixed alerts
Before you start
Critical security and failure notices are available in Free and Pro. Routine activity notification emails require the separately installed, activated Pro add-on. You need alert-management permission. Recipients must be WordPress accounts with current access to this site’s evidence and a valid account email address.
Start with a few events that require action. If you need custom thresholds, grouping or webhook destinations, use Pro advanced alerts.
Configure the essentials
Under Choose what matters, select relevant fixed rules. Examples include administrator creation or promotion and a bounded failed-authentication burst in Free. Ordinary plugin-install emails require Pro.
Under Choose who receives it, choose up to five eligible WordPress accounts. Selecting a recipient does not grant them evidence access.
Set Cooldown in seconds from 60 to 86400. For example, 3600 means one hour of suppression for repeated matching alert work; it does not stop activity collection.
If using the selected security-component deactivation rule, choose the installed components you intend to watch. This is your classification of those components, not a guarantee of their protection.
Choose Save alert settings. Reopen the page and confirm the selected rules, recipients and cooldown.
A small site wants the responsible reviewer to know about administrator promotions in Free and, with Pro, new plugin installations. Select the available rules, choose that reviewer’s authorized WordPress account and set a one-hour cooldown. Verify receipt during an already-planned staging change; do not promote a production account merely to test an alert.
Interpret delivery state
After a new matching event, inspect Recent delivery work. Alerts contain a short description and an authenticated evidence link. A queue entry is not delivery, and acceptance by WordPress mail is not proof that the message arrived in an inbox.
Cooldown suppression: repeated matches can be intentionally suppressed.
Changed configuration: new rules or recipients cancel older queued work; they do not replay old work to the new recipient.
Delivery unknown: a crashed sending attempt is not silently repeated. Check the recipient and mail-system evidence before deciding what to do.
Synthetic entries: explicitly labelled tests are tracked separately from ordinary matches.
Before sending, Logged.ai rechecks the current recipient, permission, consent and supporting evidence. A changed or revoked setting can stop a queued attempt. An interrupted attempt with an uncertain outcome is not automatically repeated; check the destination and diagnostics before sending another test.
Understand a failed or uncertain mail attempt
Free fixed alerts keep their existing maximum of three attempts when the WordPress mail call returns false, with retries after one and five minutes. If a server accepts the message but its acknowledgement is lost, a later retry can deliver a duplicate. An interrupted attempt is not blindly repeated. Mail-system acceptance is not proof of inbox delivery, and delivery is not exactly once.
Check the whole path
Confirm a relevant new event exists and matches an enabled rule.
Check the recorded delivery state and the recipient’s current evidence access.
Ask the intended recipient to confirm the message and open its authenticated link. Only that final check establishes receipt.
Nothing arrives
First separate “no matching evidence”, “no delivery work” and “mail accepted but not received”. Check rules, current recipients and cooldown, then System status and the site’s cron/mail setup as appropriate. Saving repeatedly is not a delivery test. See troubleshooting.
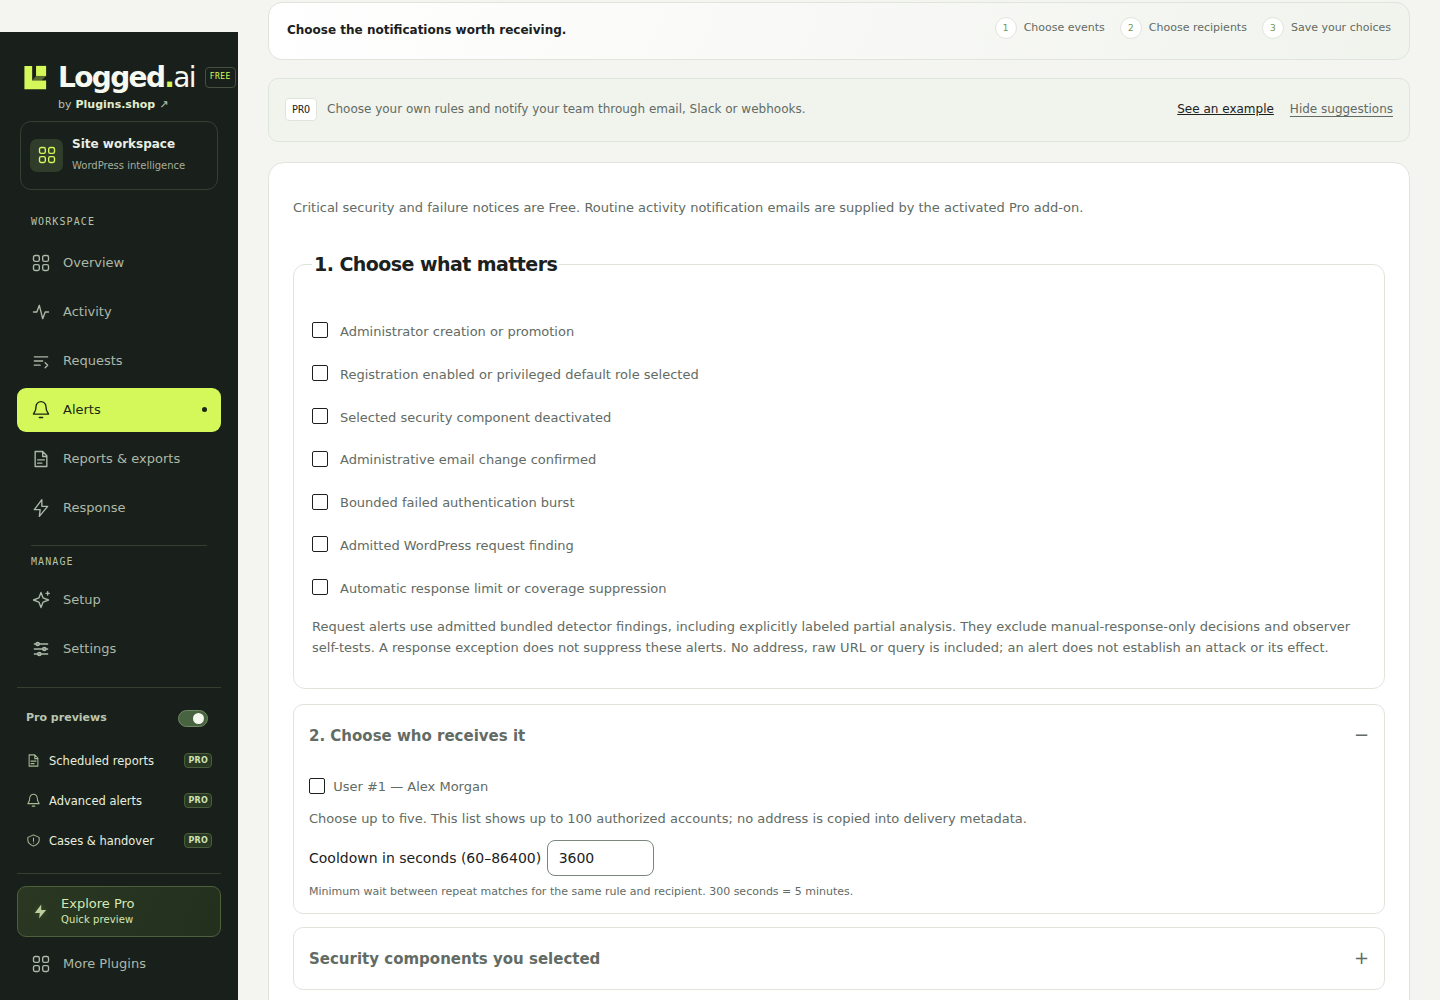
Free security notices and Pro activity emails
Free fixed email alerts
Choose critical security and failure notices and authorized recipients. All shown choices are disabled; this read-only demo sends no email.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗Pro adds routine activity notifications
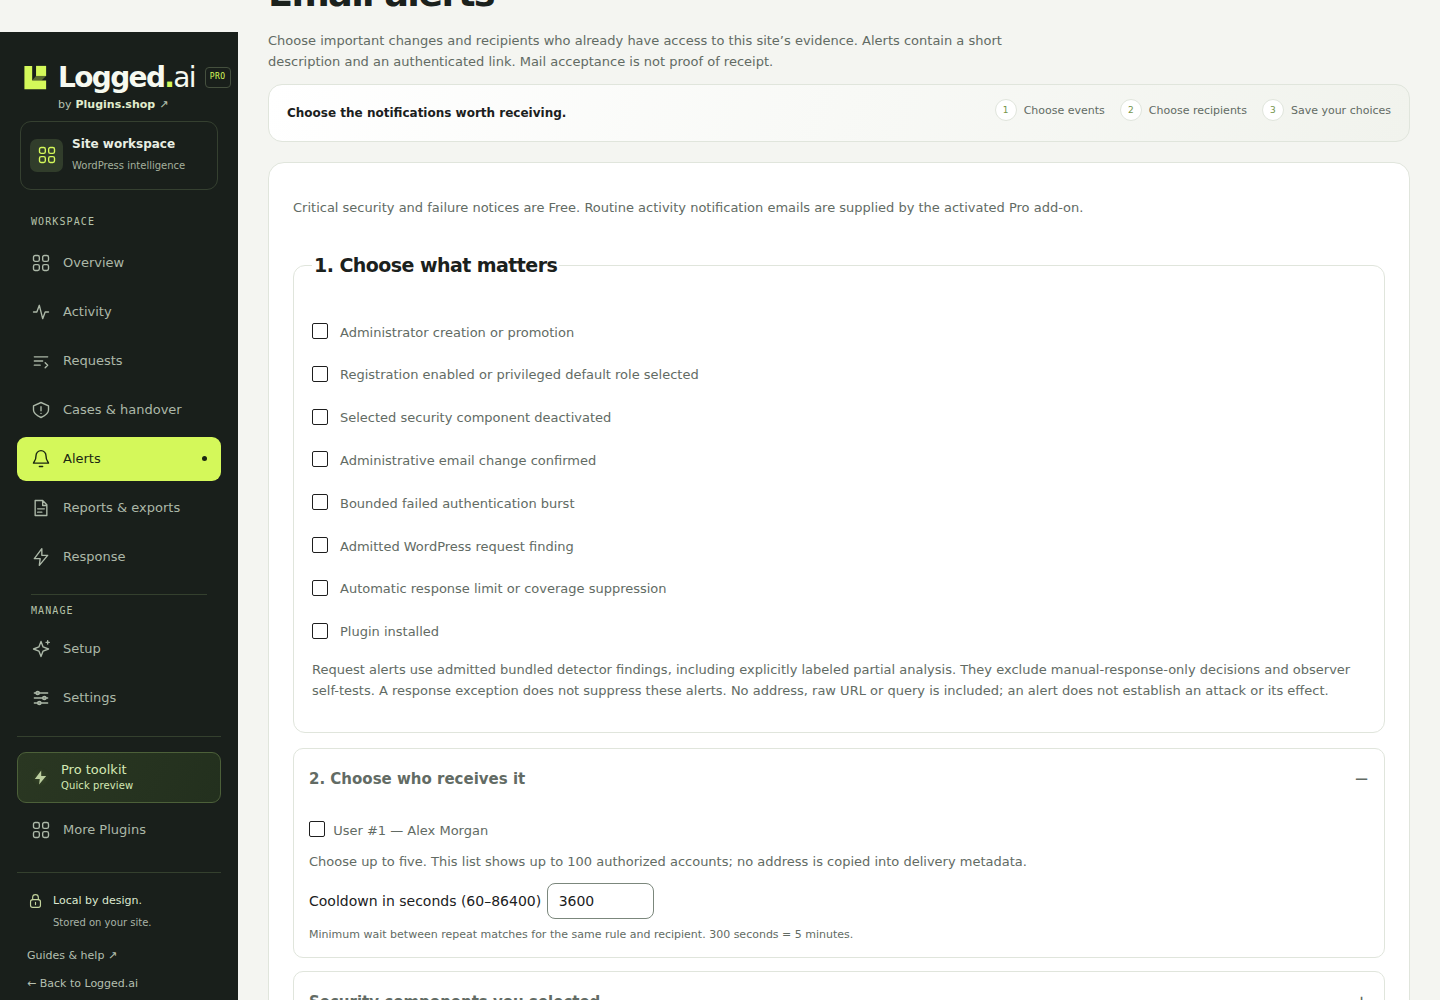
Activated Pro also provides ordinary plugin-install notices. The pictured fictional example has no enabled recipient or delivery.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Chapter 07 · Task guide · Free & Pro
Export a useful slice of evidence
Choose the right export route, narrow its scope, and verify the downloaded evidence without collecting more than you need.
By the end of this guide
You will have a useful CSV or JSON selection and understand its limits, time range and private-storage requirements.
Available in Free and Pro with export permission on the selected site. Start with the question the file needs to answer and a UTC date range. Ordinary site downloads do not include another site’s records.
A small date-based download: Reports & exports → Exports → Download now, up to 1,000 records and 2 MiB.
The filtered Activity view: Activity → Export this selection, up to 500 matching records.
A larger retained file: Prepare large export, or Create filtered background export from Activity, up to 1,000,000 rows and 256 MiB.
For a small date-based file, open Reports & exports → Exports. Under Download now, choose CSV or JSON, From (UTC, inclusive) and Before (UTC, exclusive), then download.
For person, object or other Activity filters, first refine the activity list. Open Export this selection and review its 500-record limit.
For a larger selection, choose Prepare large export, or Create filtered background export from the filtered Activity view. Read the private-storage diagnostic before creating a job.
For a background job, inspect its recorded state and download only when ready. A queued job is not a finished file.
Small direct downloads
Download now builds the complete matching result in memory. It needs no temporary export file, Sodium, Unix storage or cron. If the selection exceeds either limit, it is refused without a partial download; narrow the date range.
Example: hand over one day’s activity
Fictional handover
To include 19 October 2026 in UTC, set From to 2026-10-19 and Before to 2026-10-20. Download a small CSV for a reviewer who needs a spreadsheet. If you only need one affected account, first apply that account’s Activity filter and use the filtered route instead of exporting everybody’s activity.
Background file requirements
New saved background exports require PHP Sodium and store encrypted chunks in Logged.ai’s database tables. They expire after 24 hours and depend on WordPress scheduling; they do not require Unix filesystem permissions or writable upload directories. Keep the original WordPress authentication salts to read existing saved data. Older jobs may still use their original private file locations. Preserve those files and their original owner-only permissions until cleanup is verified; do not weaken the permissions.
Database and processing details
Both direct and saved workflows require compatible database behavior. Download now verifies privacy state using MySQL or MariaDB locking and InnoDB activity and privacy tables. A legacy MyISAM options table cannot provide that protection. Ask the host to review the diagnostic before any database change, with a reviewed backup.
Background membership is selected when its worker starts; membership and privacy are checked during bounded processing. Neither route promises a transactionally complete database snapshot. WordPress scheduling may delay a job. Native Windows has not been qualified for the saved-file workflow.
A background prerequisite is unavailable
Use Download now for a small enough date selection while the host reviews the missing prerequisite. The background diagnostic does not by itself disable activity logging or the direct route. Direct downloads can still refuse if their own database or size checks fail.
Check and handle the download
Open the file in a suitable viewer and confirm the intended site, date interval, fields and relevant records. Export dates and content retain UTC.
For a background export, retain its accompanying manifest where provided and note the job’s recorded state.
Keep the file in a restricted location and send only the evidence the recipient needs.
Deleting evidence in WordPress cannot recall a downloaded copy. Apply your organization’s retention policy to that copy separately.
If a job stays queued, use the background-processing checks. If a file is expired or no longer authorized, generate a new appropriately scoped export from evidence still available.
If a saved export fails verification
Before releasing a saved export, Logged.ai checks its metadata, encrypted chunks and complete bounded payload. Existing corruption or inconsistent records refuse output. If authority or content changes after streaming has begun, later bytes stop; bytes already received cannot be recalled and the download may be partial. Discard an incomplete file and prepare a new authorized export after resolving the reported issue.
Legacy export files on Windows
Automatic legacy-file cleanup cannot be verified on Windows. Logged.ai keeps those legacy jobs pending and stops delete-all uninstall before removing its tables. Ask your host to verify and complete the legacy cleanup outside the plugin, even if the old folders appear absent. New database-only jobs retain their database cleanup path. A cleanup warning must not be treated as proof that a file was removed.
Chapter 08 · Task guide · Pro
Work through an investigation case
Review a case’s sequence, assign the next reviewer, and leave a clear decision supported by the retained evidence.
By the end of this guide
Another authorized investigator will be able to see what you reviewed, what remains uncertain and what needs to happen next.
Where to start
Logged.ai → Cases & handover → Cases
Before you start
This guide requires Pro and investigation access on the selected site. Start from an existing case. The public Pro demo supports reading and filtering but does not save notes, assignments or statuses.
Cases organize related observations and decisions. They are not a verdict about a person, and closing one does not undo a WordPress change or activate a response.
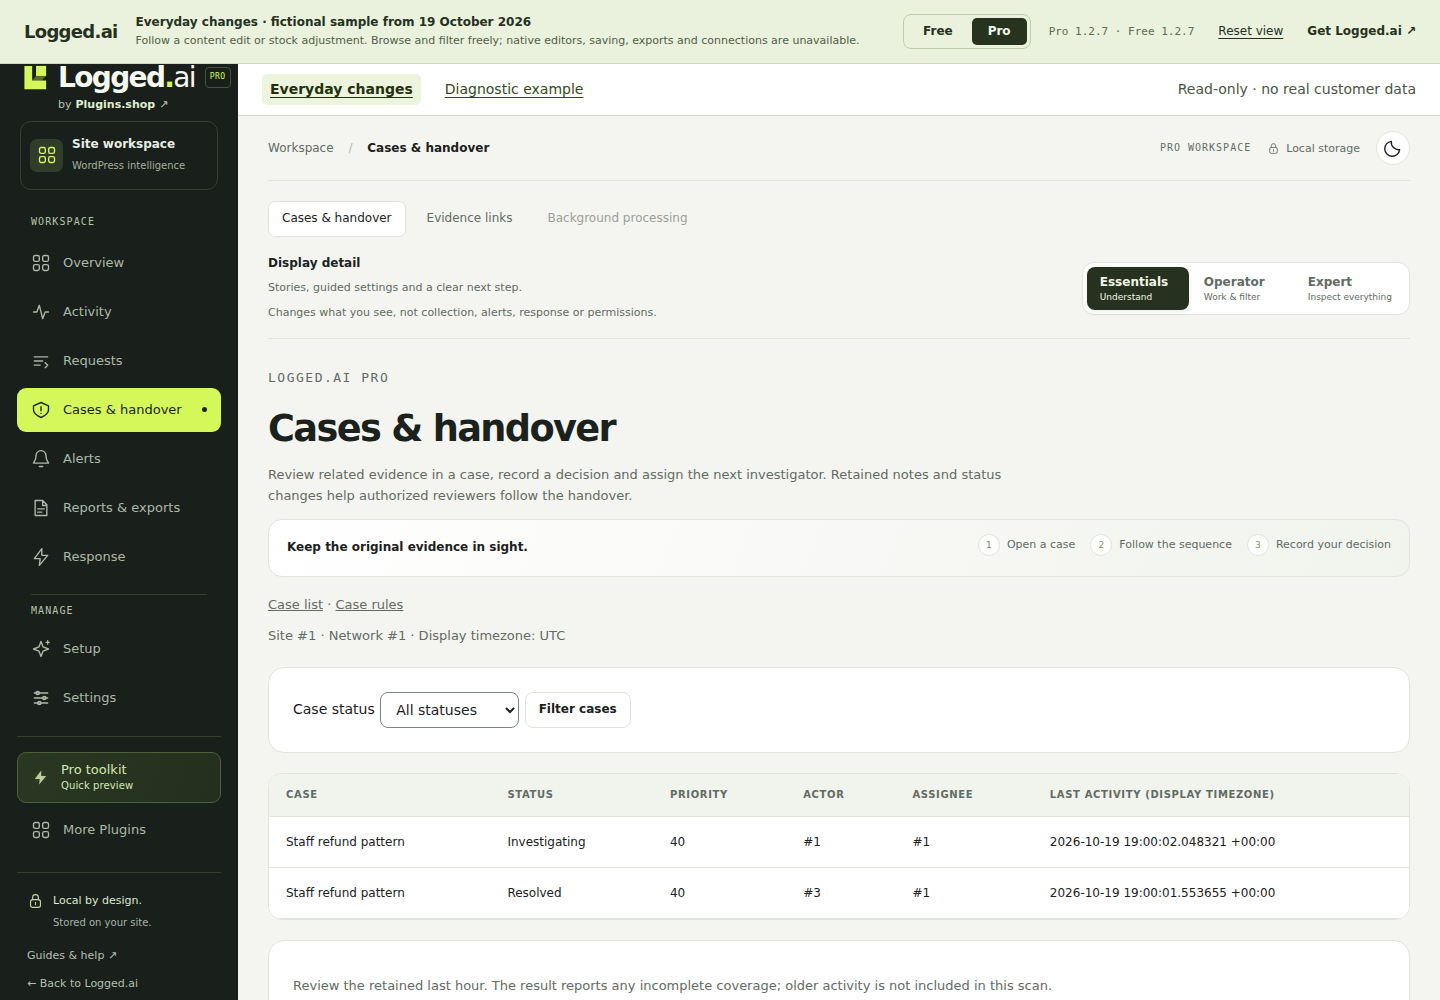
Pro Cases & handover: the case list
Filter by status, then open a case to inspect its retained evidence. Priority and associations guide a review; they do not prove intent or causality.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Review and decide
Open the Case list. Filter by Case status if useful, then open the case. Confirm its site, actor, assignee and displayed timezone.
Read Follow the sequence. Inspect retained source evidence, the priority explanation and any request-evidence links. Read Investigation history before repeating work another reviewer completed.
In Investigator WordPress ID, enter an authorized reviewer’s ID and choose Save assignee. Leave the field blank to unassign.Where do I find a WordPress user ID?
A user ID is a number, not a username or email address. If your account is already allowed to view and edit that user, open Users → All Users, find the account and choose Edit. Read the number after user_id= in the address bar: user-edit.php?user_id=42 means user ID 42. You do not need to save anything.
Your own Profile page may have no user_id parameter. If the link is unavailable or you need your own ID, ask an authorized administrator to confirm the number. Use the ID from this WordPress installation; the same number on an unrelated installation can refer to someone else. On multisite, also confirm the selected site. Do not broaden permissions just to look up an ID.
Add an Investigation note describing the evidence, interpretation and next step, then choose Add note. Keep credentials and unnecessary personal data out.
Choose the appropriate Status and select Save case status. To reopen a closed case, explicitly choose to reopen it as Open.
These are separate forms. Saving an assignee does not also save an unsent note or status choice. Reload after a successful change and confirm the retained history.
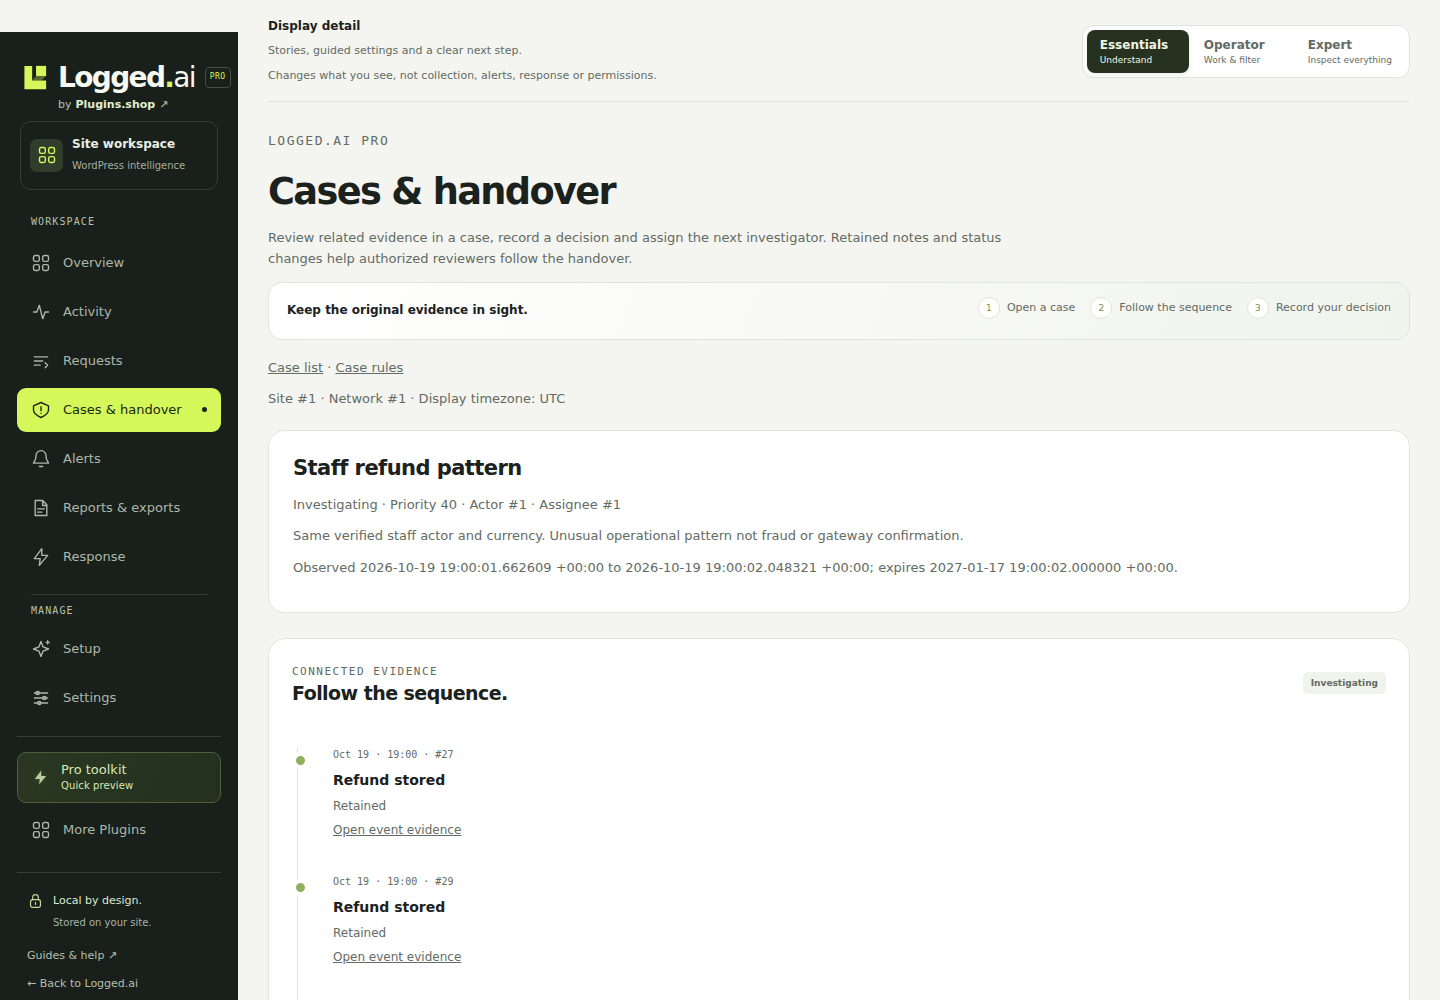
Pro case detail: follow the retained sequence
Inspect the connected source evidence before recording a conclusion. This fictional refund pattern is an operational review example, not proof of fraud or gateway completion.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.
Example: a clear reviewer handover
Fictional note
“Reviewed the retained role-change event and nearby request evidence. The role change is recorded; the address-and-time association does not establish who made the request. Need the site owner to confirm whether the role change was expected. Next reviewer: check that confirmation before closing.” Adapt the note to actual evidence rather than copying it as a finding.
Read links accurately
A shared local request identifier provides stronger context than an address-and-time association. Shared NAT, proxies and ordinary authorized activity are alternative explanations for an address link.
Priority helps order review. Neither a high priority nor a related sequence proves malicious intent, fraud or causality. Retained history records notes, assignment and status decisions; missing source evidence must stay explicit in the conclusion.
Open the exact supporting event
Use the event link in a case to open its retained Activity record in the correct site. Sign-in and current evidence permissions still apply. The link follows that event’s unique reference; another record that later reuses a numeric ID is not a replacement. Removed or expired evidence is shown as unavailable. A case note or link does not preserve the source forever or bypass retention.
If there are no cases
Confirm the site and remove any case-status filter.
Open Incident rules from the Cases page and review the configured conditions.
Open Cases & handover → Background processing to inspect the required saved configuration and explicit processing choice. Check the recorded worker state.
Compare that state with the relevant retained activity. An empty case list can mean no admitted match, unavailable processing or missing evidence; it does not establish that the site is safe.
Check the handover
The intended reviewer is saved, or the case is deliberately unassigned.
Investigation history contains the note and status decision you intended.
The note separates observed facts, uncertainty and the next action.
The case changed while I was reviewing it
Reload the current case, read the new history and reapply only the still-relevant change. A stale form should not overwrite another reviewer’s decision. See saving changes.
Chapter 09 · Task guide · Pro
Build an alert with a clear outcome
Create a destination, preview a rule against retained evidence, then separately verify the saved configuration and notification delivery.
By the end of this guide
You will know what the rule matches, where it sends minimized facts, whether it is enabled and what the delivery check actually proved.
Where to start
Logged.ai → Alerts → Advanced alerts
Before you start
Requires Pro and the relevant alert and investigation access on this site. Start with a single recipient or destination and a clear event condition. Use Free fixed alerts when its predefined email rules already cover the need.
Destination storage requires PHP Sodium and a valid private alert encryption key. Ask the server administrator to follow the one-time setup panel and preserve any existing key. Replacing the key can make encrypted records unreadable.
The read-only public demo shows a disabled fictional rule and destination. It cannot save configuration, enable alerts or send tests. The example below illustrates the current rule editor; it is not evidence of real message delivery.
Prepare the destination
Complete Set up storage if offered. This creates no enabled rule or destination by itself.
Add a meaningful label and choose WordPress email, signed HTTPS webhook or Slack webhook. For email, choose an eligible WordPress recipient; for a webhook, provide its intended secret URL.
Review the consent to send minimized alert facts, choose whether to enable the destination, then select Save destination. Saving does not send a notification.
If a signing secret is shown, store it privately now. The webhook signing secret is displayed once.
Recipient or webhook requirements
Email recipients need current event and investigation access and a valid email. Use Find an email recipient if the intended eligible account is missing from the bounded list. Webhooks require a public HTTPS destination on port 443; unsupported transport platforms do not send. Treat Slack URLs and signing secrets as credentials.
Preview and save the rule
For a supported severity rule, use the readable builder to choose its condition, window, minimum count, grouping, cooldown, alert severity and destination. The declarative source remains authoritative for compound rules.
Choose Preview expression. Review both matching-source counts and groups that reach the threshold. A preview examines a bounded retained sample; it neither saves the rule nor sends a notification.
Review the draft’s enabled state. Leave replay unchecked unless you deliberately want retained sources within the rule’s time window to produce new notifications.
Choose Save rule version. Confirm the saved revision, enabled/disabled state and destination. A preview result alone is not a saved rule.
A useful starting example
The supplied default is a high-or-higher severity condition, a 300-second window, a minimum count of 1, site grouping and a 300-second cooldown, initially disabled. Select a real destination, preview the sample and adapt those values to your review process before enabling it.
An exact-event rule in Pro 1.2.7 displays the readable event name, such as Content created, in its saved-rule title. Existing exact-event rules keep their saved conditions, destinations and revision history; the title correction does not enable a rule or change its matching behavior. Compound conditions can still use a generic title: inspect the preserved source and preview before saving.
Pro advanced alert: an exact-event condition
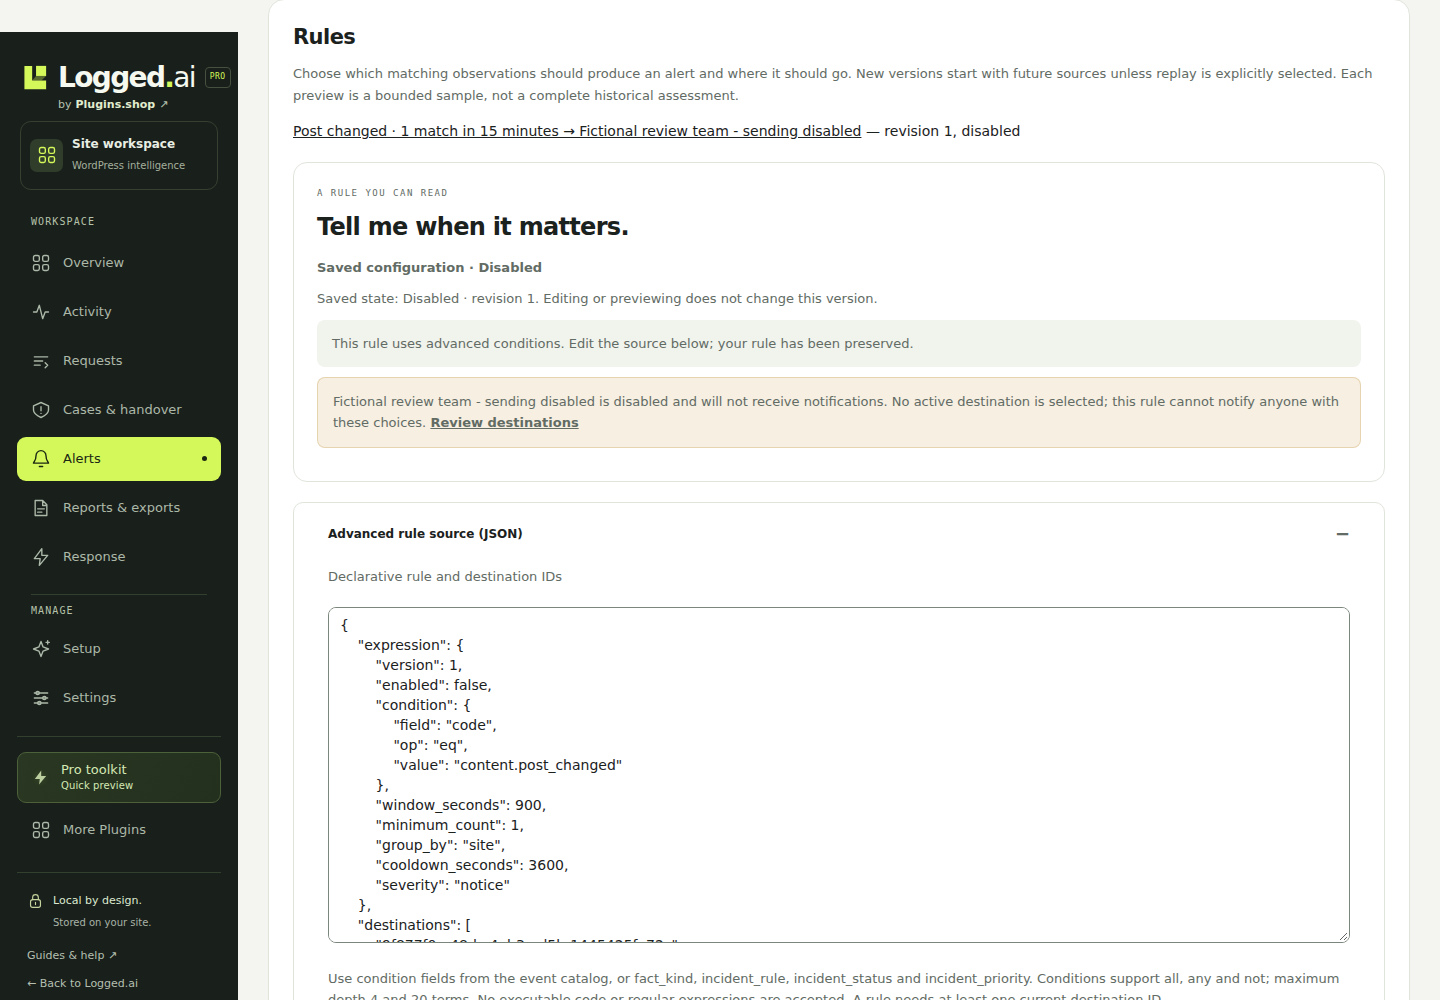
The supported event condition appears as Post changed. This fictional rule and its destination are disabled; the example does not send a test or enable delivery.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Verify delivery and avoid surprises
For an enabled destination, explicitly authorize one Queue synthetic test. This intentionally sends a labelled test to that destination.
Inspect Recent delivery history: distinguish Synthetic test from Rule match, and read status, attempts, acceptance and reason.
Confirm receipt with the recipient or receiving system. Accepted means the transport or WordPress mail subsystem accepted the attempt, not that the message reached its destination.
The synthetic test checks the destination path; it does not establish that a future event will satisfy the rule. The rule still needs suitable evidence, processing and an enabled, available destination.
Editing a webhook requires its URL again, rotates its signing secret and invalidates queued messages for the prior revision. Unknown advanced-delivery attempts may retry with the same delivery ID, so duplicates are possible.
Follow the alert back to its evidence
A real advanced-alert email can link to its triggering event or case. Recent delivery history → Open supporting evidence opens retained references for that rule match. Sign in with an account allowed to review the relevant site and evidence. Removed or expired references remain unavailable; a Synthetic test has no real triggering event. Transport acceptance and an accessible evidence link do not prove inbox delivery.
Read the delivery result conservatively
Mail checks apply to the alert’s own WordPress mail call, including its current message and recipient after final authorization. Other extensions’ nested mail calls are separate. A suppressed or uncertain result is not evidence that the intended inbox received the message. Previously sent messages cannot be recalled.
If the outcome is not what you expected
The preview is empty
Check the condition, threshold and time window against evidence still retained. The preview is bounded, so zero matches in its sample is not proof that the event never occurred.
The draft cannot be saved
If settings changed since you opened it, keep any necessary nonsecret edits, reload the current saved rule and review the changes. Do not try to bypass the revision guard.
The rule saved but no notification arrived
Check both rule and destination enabled states, then matching evidence, cooldown and Recent delivery history. Follow the recorded reason. A successful save, a preview and a synthetic destination test each prove a different part of the workflow.
Chapter 10 · Task guide · Pro
Make a useful review repeatable
Turn a useful review into a saved search, verify one private report, then add a schedule with a deliberate time period and recipient.
By the end of this guide
You will have a reusable search and know which evidence its reports include, when scheduled periods run and how long private copies remain.
Where to start
Logged.ai → Reports & exports → Saved searches and reports
Before you start
Requires Pro and investigation access on the selected site. Start with filters that already answer a real question. You must own the saved search to create its schedule; sharing a search does not grant other people evidence access.
Complete the local reporting-workspace check if offered. It does not email a report. Reports use their own encrypted database storage and prerequisites, separate from Free’s on-demand exports.
Save the view and verify one report
Choose New saved search. Give it a useful title and select a report type: site activity, user activity, sensitive changes, authentication, WooCommerce or incident cases/local summary.
Set only the necessary filters. User activity requires the actor’s WordPress ID. For incident reports, clear activity filters and use the case-status filter.Where do I find a WordPress user ID?
A user ID is a number, not a username or email address. If your account is already allowed to view and edit that user, open Users → All Users, find the account and choose Edit. Read the number after user_id= in the address bar: user-edit.php?user_id=42 means user ID 42. You do not need to save anything.
Your own Profile page may have no user_id parameter. If the link is unavailable or you need your own ID, ask an authorized administrator to confirm the number. Use the ID from this WordPress installation; the same number on an unrelated installation can refer to someone else. On multisite, also confirm the selected site. Do not broaden permissions just to look up an ID.
Choose Only me or Investigators on this site, then save. Keep credentials and personal information out of the title.
Open the search and inspect its current results. Under Generate a report, choose the UTC period and CSV, JSON or HTML.
Check the report’s generation state before downloading. Open the file and confirm it answers the intended question before setting up repeat delivery.
The requested period intersects the saved filters and current retention. A saved search with a fixed old date range will not automatically become a rolling review.
Start with the Activity filters you already chose
In Activity, choose Save this Activity view. Pro opens a separate tab at Save this Activity view, with supported filters copied into an unsaved, private form. Review those filters, enter a useful title, keep or change visibility deliberately, confirm the displayed site and choose Save search. Until you save, no search exists. Opening this form does not create a report, schedule or alert, and the original Activity page keeps its state.
The shortcut cannot carry the free-text Find a type of change query. Replace it with the appropriate Recorded action filter before using this shortcut. Review absolute UTC date bounds carefully: a saved old interval will stay fixed. In saved-search results, use the event link to inspect the exact retained evidence with your current permissions.
Pro saved searches: start with a useful review
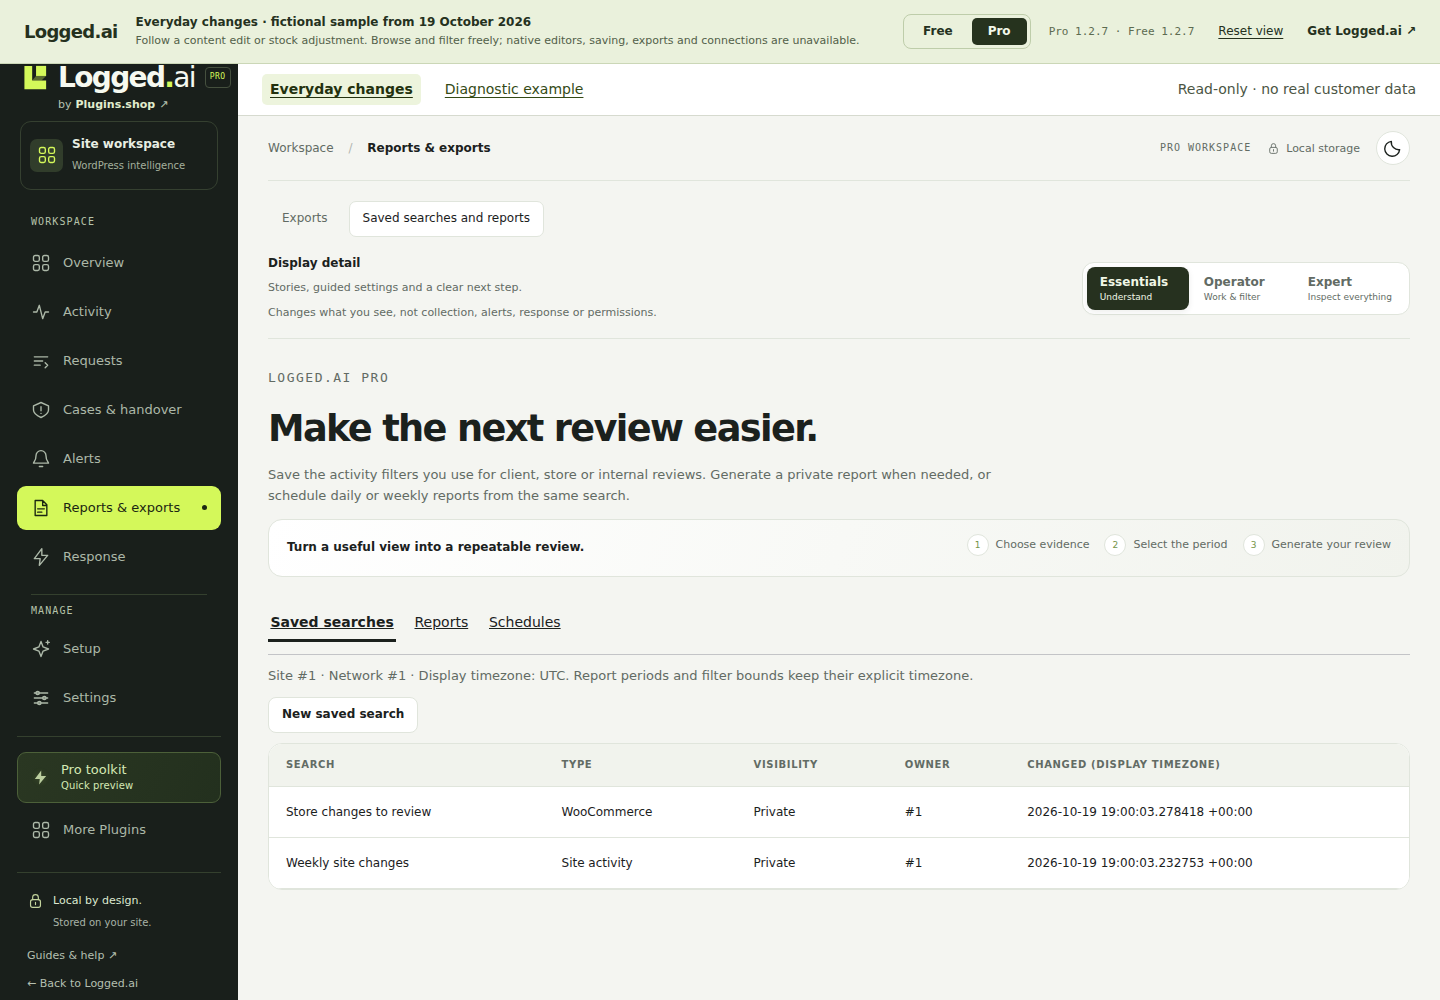
Two fictional saved searches illustrate reusable review scopes. Inspect each search’s filters before generating a report or creating a schedule; opening it does not send anything.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Example: a weekly sensitive-change review
Fictional review
Create a search titled “Weekly sensitive changes” using the sensitive-changes report type. Leave absolute date bounds blank if you want each scheduled period to choose the time range. Generate one manual report for a known UTC interval and inspect it. Once its scope is right, add a weekly schedule at a chosen local hour in the team’s named timezone.
Schedule the review
Open Schedules → New schedule and select your saved search.
Choose daily or weekly cadence, local hour, named timezone and output format. Daily reports cover the previous local day; weekly reports run on Monday for the previous seven local days.
Choose whether to enable the schedule and send a minimal summary to your current WordPress account email. Acknowledge the seven-day private report copies, then choose Save schedule.
Inspect the saved schedule and recorded report-job state. WordPress cron depends on the site’s runner; the selected hour is not a guaranteed inbox delivery time.
Daylight-saving changes and late workers
A repeated clock hour creates one period; a skipped hour runs after the jump. Late workers consider at most seven intended delivery days. Check the named timezone and the recorded period instead of assuming a fixed UTC hour.
Pro schedules: check whether delivery is enabled
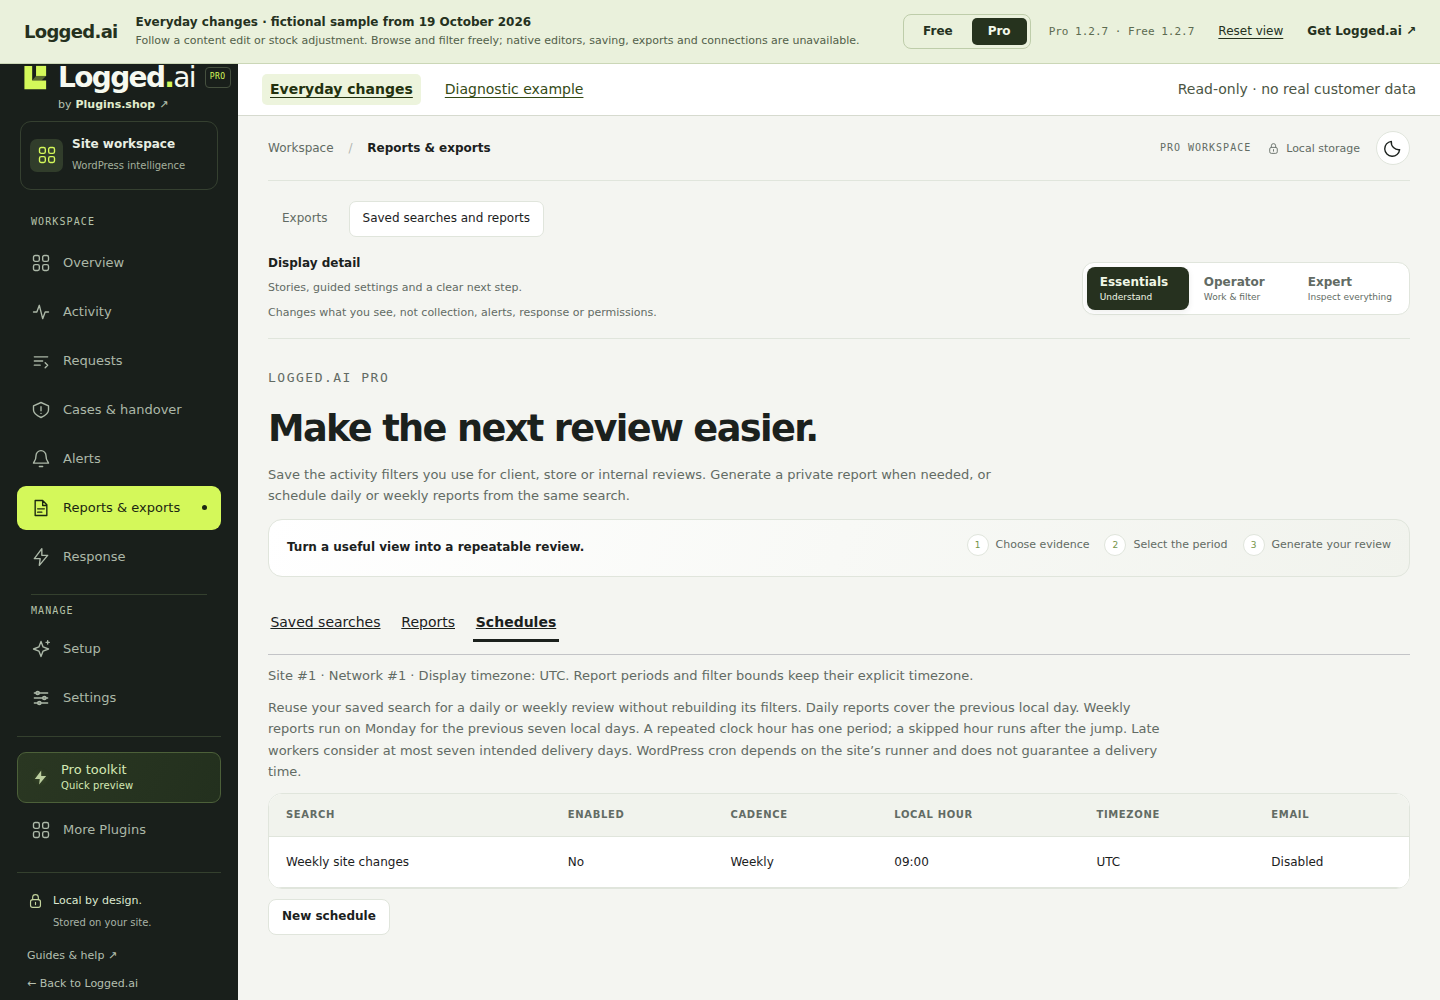
The example review is weekly at 09:00 UTC, with the schedule and email disabled. On your site, enable them deliberately only after verifying a manual report.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Understand what is retained
A report contains bounded source membership, not a complete database snapshot. The limit is 10,000 records and 16 MiB.
Private report copies expire after seven days. Downloaded copies need their own appropriate retention handling.
Email contains a minimal summary and authenticated link, not a report attachment. Mail acceptance alone is not proof of receipt.
Removing a saved search also cancels its reports and removes its schedules. Review that consequence before deleting it.
Handle an unavailable report
A saved report’s manifest and job details must agree before its output is offered. A damaged or inconsistent report can remain visible with Records unavailable; an authorized owner can cancel it while healthy reports stay available. Cancellation does not recover missing evidence or recall a downloaded file. Generate a fresh appropriately scoped report from evidence still retained.
Pro report notifications make one mail attempt. A transport acceptance does not prove inbox delivery, and an uncertain notification is not automatically resent. Report lists are bounded views whose selected rows are rechecked; they are not a transactionally complete snapshot of the database.
Check the next run
Confirm the saved search still returns the expected kind of evidence and the schedule is enabled if intended.
Verify the recorded period, generation status and any email state separately.
Open the generated report while it is available. For a notification, have the owner confirm receipt and access to the authenticated link.
The report is empty, delayed or unavailable
For an empty result, inspect the intersection of saved dates, report dates and retention. For delay, check the schedule, timezone and cron status. For an expired or inaccessible report, use current authorized evidence to generate another. See troubleshooting.
If Attempting remains visible: the delivery outcome is uncertain. Logged.ai does not automatically repeat that attempt, because a message may already have been accepted. Check the authorized destination and delivery diagnostics before deliberately creating another notification. A report remaining available does not prove its email reached an inbox.
Chapter 11 · Task guide · Pro connection
Activate Pro and manage updates
Activate your licence once for this site, then keep the matched Free and Pro pair up to date. Know what happens when you renew, move a licence or remove its saved connection.
By the end of this guide
You will unlock Pro for the correct site, understand what activation sends, and choose the right update or licence-management action.
Where to start
Logged.ai → Licence & updates
Activate Pro on this site
Install and activate Free first, then the compatible Pro add-on. WordPress plugin activation loads the add-on. On a new installation, the first successful licence activation unlocks new Pro work for this site; uploading a Pro ZIP alone does not unlock it.
Open Logged.ai → Licence & updates. Check that the displayed site address is the site you intend to register.
Copy the licence key from your account. Read the disclosure, enter the key, tick the consent box and choose Activate Pro.
Check the result. Continue into reports, alerts or cases. Opening a workflow never enables an alert, schedule or response automatically.
If an earlier installation shows Preserved for this existing installation, choose Connect licence for updates to add an eligible licence. Its retained local access does not need a new activation merely to continue on the same site.
The supplied publisher configuration is ready to use; a normal installation does not need an edit to wp-config.php. Keep licence keys out of screenshots and support messages.
What activation and updates require
Activation uses WordPress HTTPS with outbound access to plugins.shop. It does not require Linux, a separate PHP command-line installation, curl.so or process/POSIX functions. The native Sodium extension is not required for activation: WordPress’s bundled compatibility library can protect the saved credential.
In-plugin ZIP installation also needs the PHP ZIP extension, writable private temporary storage outside public web roots, and normal direct WordPress permission to update plugin files. The update screen reports an unavailable requirement. Account ZIP downloads remain the alternative installation route; they do not bypass first licence activation.
Only the licence key, product identifier, operation and this site’s canonical home URL are sent for licence actions. Audit events, request evidence, visitor data and case contents are not sent. Viewing the licence page does not contact the service.
Separate features such as saved private exports or arbitrary webhook destinations have their own storage and delivery requirements. Check the relevant guide before enabling them.
Use a normal site hostname with HTTPS on port 443 for activation and update checks. Custom ports such as localhost:8080 are not supported by the licence service. Use a disposable staging hostname when testing a real licence; do not copy a customer key into a public demo.
Keep an activated workspace available
After a successful first activation, the saved local grant keeps Pro available through expiry, temporary service outages and later remote invalid or revoked status. New activations, private downloads, updates and product support still require the appropriate commercial entitlement. Existing evidence remains subject to your normal permissions and retention choices.
Upgrading an existing installation: a Pro installation initialized before 0.1.8 retains local access on its current canonical site and environment. This continuity record is not proof of purchase, does not reserve a licence slot and never grants paid updates. You can connect a valid licence for paid updates and support. A verified existing same-site commercial connection also preserves its recorded activation.
Moving an installation to another address or service environment requires activation. Copies made before their first migration, or exact copies sharing the same address and identifiers, cannot be identified automatically. A failed update lookup does not remove an existing local grant.
Check and install an update
These steps cover the compatible Free 1.2.7 and Pro 1.2.7 packages. Check availability before starting; a release note or screenshot does not mean that an updater offer is available.
Open Pro updates, confirm use of this site’s saved connection and select Check Pro updates. A service offer lasts 15 minutes; a fresh lookup can require a five-minute cooldown.
Install the matching Free update first, then use WordPress’s Update now action for Pro. Complete both before resuming Pro work. Background automatic Pro installation is disabled.
Check the installed versions, System status, any saved schema-upgrade phase and one representative workflow. Do not uninstall as an update method.
Manual route: obtain the matching Free and Pro ZIPs from your account, then replace Free first and Pro second through WordPress. An already activated site retains its activation during an ordinary compatible-file update.
The private updater checks the installed Free version against the offered package’s compatibility metadata, plus the supported schema, commercial entitlement and archive. For the 1.2.7 pair, install Free 1.2.7 first. If no compatible Pro offer is available, use an authorized account ZIP when that version is available. An offer alone is not installation approval. If an update fails after WordPress has deactivated Pro, inspect the installed files and plugin state before retrying; keep Free active.
Move or remove a licence connection
The uncommon actions are under Manage this site’s licence. Read their effects before confirming.
Release licence slot
Ask the service to release this site’s slot so it can be used elsewhere. New Pro work locks here only after the service confirms the release. If the request fails, the saved local activation remains.
Remove saved connection
Remove this site’s saved key and local activation immediately. New Pro work locks here, even if the service is offline. This makes no service request and does not free the account’s site slot.
When an earlier installation has no saved licence, the same local action is labelled Turn off preserved local access. It withdraws that retained access immediately; a later successful activation is needed to unlock new Pro work.
Neither action deletes existing evidence or stops Free collection. Both withdraw local activation or retained installation access: new imports, Pro processing, scheduled report generation and advanced-alert generation or delivery stop. Authorized existing records/downloads and available privacy, cancellation and disable controls remain accessible. Existing request rules and already installed response policies keep their scope and expiry; disconnection does not recall completed actions or delivered messages. Review saved and pending work before reactivation.
Uninstalling Pro also removes its saved credential, local activation and installation identity without releasing the remote slot. Reinstalling requires successful activation. Default uninstall retains investigation data and a nonpersonal withdrawal marker; explicit delete-all removes both. Use Release licence slot before uninstalling when you need to move the allowance. Updating by replacing plugin files preserves ordinary existing access.
Activation or an update is unavailable
Check the displayed site address, key, site allowance, outbound HTTPS and the named hosting requirement. Preserve the nonsecret diagnostic code if you need support. Do not change the site identity or weaken a storage permission to bypass a check. If the old site is inaccessible, ask support to help with its licence slot.
Updating to 1.2.7: first confirm that the release is available from the download page and your account. Back up and test the compatible pair on staging. In WordPress, choose Plugins → Add New Plugin → Upload Plugin → Replace current with uploaded. Replace Free first, then Pro in a separate upload; keep Free active and do not uninstall either plugin. Free-only sites replace only Free. An update offer is separate from a successful installation and must pass the usual compatibility, entitlement and archive checks.
Chapter 12 · Reference · Free & Pro
Display detail and saving changes
Choose a comfortable view, tell a draft from a saved setting, and check that your change actually took effect.
Where to start
Display detail control on Logged.ai workspace pages
Quick answer
Display detail changes what you see. Only a form’s Save or Apply action commits that form’s configuration.
Free Overview and display detail
Essentials, Operator and Expert are available in both editions. Display detail changes presentation, not permission or collection.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo ↗
Choose a view for the task
Which display detail should I use?
Choose
Best for
What changes
Essentials
Understanding an event or finding your next step.
Readable stories and guided controls.
Operator
Regular review, filtering and configuration.
More working controls and filters are visible.
Expert
Inspecting precise values, source detail or diagnostics.
Additional technical detail is visible.
All three levels are available in Free and Pro. You can still open individual details at any level. Changing the view does not change collection, alerts, response policies, evidence or permissions.
Try it without changing evidence
Open the Free demo and switch between Essentials and Operator. The demo’s fictional sample supports browsing; saves and exports are unavailable.
Know what is saved
Draft, preview and saved state
What you see
What it means
What to do
Unsaved changes
Edits are still in that form. The previously saved configuration remains in effect.
Review the changes, then use that form’s Save or Apply button.
Preview result
You have inspected a proposed result; this does not save the configuration.
Return to the draft, confirm it is correct and save deliberately.
Undo edits
The form returns to its saved values.
Use it to discard the current edits before starting again.
Conflict or stale-form error
The server did not confirm your requested change against the current version.
Reload the current settings, compare them and reapply only what is still needed.
After saving, read the result message and any enabled/disabled or destination state.
Reload the page and check that the saved values match your intention.
For an alert or response, also follow its own preview and verification steps; a saved setting alone does not prove delivery or enforcement.
Changing Display detail keeps the current form and its edits open. Browser appearance preferences are separate from server configuration; do not rely on an unsaved form surviving a page reload.
Workspace groups Overview, Activity, Requests, Alerts, Reports & exports and Response. Activated Pro also includes Cases & handover. Manage contains Setup and Settings. The links you see still depend on your permissions and the current site.
In Free, the Pro previews switch hides or restores the three examples: Scheduled reports, Advanced alerts and Cases & handover. The switch stays visible and saves the choice for your administrator account on this site. Explore Pro remains below the group. Settings also provides controls for optional suggestions.
Activated Pro shows Pro toolkit instead of the Free preview group. Opening guidance does not enable alerts, schedules or response rules. More Plugins opens a locally bundled catalogue; it does not install another plugin or request an external catalogue. Visiting a product’s website is a separate link.
Changing the saved preview preference requires JavaScript. Without it, visible preview links open their normal local preview pages. In the public fictional demo, the switch changes only the current demo tab; it does not save an administrator preference.
Chapter 13 · Reference · Free & Pro
Collection, attribution and coverage
Understand what Logged.ai records, what the fields mean, and how to read missing or incomplete evidence.
Use a record to explain an observed operation. A missing record, a request finding or a summary count cannot prove everything that happened on the site.
01Actor
Who performed the action?
02Subject
What did it affect?
03Outcome
What was observed?
Collection and filters do different jobs
Choose the control that matches your intention
I want to…
Use
Effect
Find an existing change
Activity filters
Selects from records already retained. It does not change future capture.
Changes when older evidence becomes eligible for cleanup; shorter retention needs separate confirmation.
See more detail on the screen
Display detail
Changes presentation only.
Collectors cover supported WordPress accounts, content, settings and components, plus supported WooCommerce activity. Generic WordPress hooks do not provide dedicated coverage for every SEO, form, membership or custom-field plugin.
A preset can change both optional categories and administrative-event retention. Review its proposal before applying it; a troubleshooting preset is not a read-only filter.
Read actor, subject and outcome separately
How to interpret a record
Term
Meaning
Keep in mind
Actor
The account or execution context that performed the observed operation.
Background or unknown context must not be reassigned to the administrator reading the screen.
Subject / affected object
The account, post, setting or other object affected.
The affected person can be different from the actor.
Outcome
The result observed by that collector.
An attempt, failure and successful change are different results.
Captured field differences
The supported before/after detail retained for that event.
Sensitive values can be minimized or unavailable; not every field has a full value history.
Example: Alex changes Maya’s role
Alex is the actor; Maya is the affected account. Check the observed result and role difference before concluding that the requested change succeeded. Current profile labels are not a historical profile snapshot.
A deleted user can leave an identifier without a current profile. Keep that uncertainty in your notes and handover.
Current navigation context and recorded evidence
Content titles and native editor links are looked up using your current access to help navigation. They are separate from the event’s stored and exported evidence. A revision link refers to the exact retained accessible revision, not a reconstructed copy. Compact price, stock and order differences use the recorded values only; missing or redacted values remain explicit. Item-history and Pro evidence links show retained records in the correct site, not a promise that every past action was collected.
Minimized fields and local integrity
Slug, date, comment and pingback change markers preserve the fact of a supported change without retaining those raw values. Current navigation labels stay separate from the stored record. Report/export consistency checks can detect damaged or mismatched records; they are not signatures against an equally privileged operator who can alter coordinated database values.
Know what the evidence cannot answer
Overview cards and the activity map summarize retained samples. They are not a complete traffic count or a map of your network.
Request minute groups count admitted observations, not unique attackers. A finding describes a pattern; it does not prove intent or successful exploitation.
Traffic handled by a cache, CDN or server before WordPress may be invisible to the WordPress observer.
Events before activation, unsupported direct database edits, collection gaps and evidence already removed by retention cannot be reconstructed from this log.
Local storage is not independent, tamper-proof evidence storage.
If something is missing
Check the site, filters, collection choices and retention first. Then use the troubleshooting reference to inspect collection health and request-source coverage.
Why one failed sign-in can leave no Activity row
Failed sign-ins are grouped: ten observed failures in the same fixed five-minute interval create a burst entry. Fewer failures have no individual Activity entries. Intervals restart every five minutes, so attempts on different sides of a boundary count separately. Supported WordPress failures against an existing account can also create a separate account-targeted burst. This identifies the account targeted, not the person attempting to sign in; passwords and attempted login text are not retained.
Requests contains matching findings, not a complete sign-in or traffic log. An upstream block or unsupported authentication integration may never reach the supported WordPress hooks. If an expected burst is missing, inspect System status and collection coverage.
Chapter 14 · Reference · Free & Pro
Privacy, retention and erasure
Choose what address detail to retain, understand when evidence is removed, and distinguish a routine update from irreversible deletion.
Where to start
Logged.ai → Settings → Privacy and retention
Quick answer
Filtering, deactivating and deleting are different actions. Review the scope and confirmation before shortening retention, erasing a person’s evidence or enabling deletion on uninstall.
Choose address privacy intentionally
Request IP mode
Mode
What is retained or shown
Practical effect
Masked (default)
Shared network context from the derived connection address.
Useful context, not an exact person or device identity.
Full derived address
The address derived under the configured source rules, until its separate expiry.
An explicit choice; exact-source targeting also needs trusted, eligible address context.
Disabled
No address context.
Source targeting is unavailable.
The direct connection address is used by default. Forwarded headers require an explicitly configured trusted-proxy boundary. An address is not proof of a person’s identity, and no IP pseudonym is retained.
More private modes immediately restrict display and export. Removing older stored copies happens through bounded cleanup. Administrative activity collectors do not retain IP addresses.
Set retention, then check cleanup
Open Settings → Privacy and retention and review the currently saved periods.
If shortening a period, read the affected-data explanation and confirm irreversible removal. This requires separate evidence-purge permission.
Choose Save privacy settings, then read Retention status. Cleanup runs in bounded batches and can be delayed if scheduling is stopped.
Use Prune expired events only when you intend to remove one expired batch of administrative evidence from the current site. It is not a preview.
Default periods in a new 1.2.7 installation
Product defaults; your saved values may differ
Evidence
Default retention
Administrative events
90 days
Request observations
7 days
Request groups
30 days
Inactive response history
30 days
Full exact client addresses
14 days
Diagnostics
7 days
Collection presets or an administrator can change these values. Product defaults do not determine your legal or business retention obligations.
A longer period cannot restore deleted records
Increasing retention affects evidence still available and future collection. Previously removed evidence does not reappear.
When privacy settings cannot be read safely
Privacy-sensitive downloads and cleanup use fresh saved policy with local coordination. A busy operation can return a retryable error. Unreadable privacy settings disable address capture and pause activity/request cleanup instead of silently applying fallback retention. Review and save valid settings to repair the problem, then check System status. Historical health messages are not erased by a repair.
Handle a personal-data request in the correct site
WordPress privacy actions
Action
What Logged.ai does
Boundary
Export Personal Data
Supplies a protected reference for an authorized administrator to review associated evidence.
The ordinary WordPress download does not receive a copy of the activity records.
Erase Personal Data
Removes matching evidence and linked request-address context through scoped cleanup.
Requires WordPress privacy permission and evidence-purge authority; it does not delete the WordPress account.
Request for a deleted account
An authorized operator uses the known former user ID through the scoped privacy CLI.
An email lookup cannot recover the old account ID. Other sites need separate authorized handling.
Check the reported completion state. Cleanup may need more than one batch, and a zero event count does not prove that every related piece of personal data has disappeared.
Files already shared remain outside this cleanup
Downloaded exports, reports and copies held by recipients cannot be recalled. Include those copies in your own handling process.
Deactivation, updates and uninstall
What happens when you stop or remove the plugin?
Action
Data effect
Deactivate
Retained data is preserved.
Update the plugin ZIPs
Use the normal update path; uninstall is not required.
Uninstall with deletion disabled
Retained data is preserved.
Uninstall after explicitly saving installation-wide deletion
Logged.ai data across the installation, including its sites and networks, is selected for deletion. This needs installation-purge authority and confirmation.
Legacy export cleanup: explicit delete-all uninstall removes owned tables only after private export cleanup is verified. On Windows, automatic verification of legacy files is unavailable, so their job records and the plugin tables remain until host-assisted verification and cleanup outside the plugin. This safeguard does not prevent ordinary database-only expiry cleanup. Read the export storage requirements before removing old files.
Chapter 15 · Reference · Free & Pro
Site, network and permission boundaries
Find the workspace that owns the evidence and understand why viewing a page does not grant every action on it.
Where to start
Site Admin → Logged.ai; Network Admin → Logged.ai
Quick answer
A site workspace covers that authorized site. Network Admin has a separate view of network-origin evidence; it does not merge every site’s timeline.
Choose the workspace that owns the action
Where should I look?
What you are reviewing
Open
Scope
An action inside one site
That site’s Admin → Logged.ai
The current authorized WordPress site.
An action from network administration
Network Admin → Logged.ai
Evidence originating in the current network’s administrative context.
A network-origin export
Network Admin → Logged.ai → Exports
Network-origin evidence; not a combined export of all sites.
An unrelated client installation
That installation’s own WordPress admin
Multisite views are not a remote dashboard for separate installations.
Use the WordPress site switcher when you need another authorized site. Shared plugin, theme or WordPress files can affect multiple sites even when the recorded action originated in a network workspace.
Match permissions to the job
Separate abilities in the workspace
Task
Why viewing alone is not enough
Change collection or privacy settings
Settings authority is checked separately.
Download evidence
Export authority is checked separately.
Inspect sensitive address context
The account needs the relevant sensitive-context grant.
Manage alerts or response
The corresponding management authority is required.
Shorten retention or purge evidence
Deletion needs its own evidence-purge authority and confirmation.
Navigation shows registered pages the current account can access. Pro investigation and reporting workflows also check evidence authority. A saved search, shared link or Pro installation does not grant missing permissions.
Confirm the account and selected site or network.
Check that Free and the compatible Pro package, when needed, are active.
Ask the site administrator to review the specific missing permission; avoid granting broad access just to make a button appear.
Example: a teammate can view Activity but cannot export
This can be an intentional permission boundary. Their ability to read a record does not automatically authorize a downloadable copy.
Check your own multisite arrangement before rollout
Use a staging copy that represents your WordPress and WooCommerce setup.
Test one site action and one network action; confirm each appears in the expected workspace.
Verify viewing, export and deletion boundaries using the actual roles your team will use.
Keep commercial site allowances separate from WordPress permissions; a licence allowance does not change capabilities.
The packages have scoped multisite behavior, not a guarantee for every host, extension or network arrangement. Preserve each site’s own privacy and retention requirements.
Chapter 16 · Reference · Free & Pro
Troubleshoot without losing context
Start with the symptom, check the relevant state, and gather a small support record without exposing private evidence.
Where to start
Logged.ai → Settings → System status
Quick answer
Check the specific record, job or destination before retrying. “Pending,” “accepted” and “complete” describe different stages.
Start with the symptom
Symptom → check → next step
What you notice
Check first
Next step
A change is missing from Activity
Correct site, active filters, optional collection categories and retention.
Reset filters, then inspect Settings → System status. See coverage limits.
A request is missing
Requests → Source and verification, then the Observer self-test.
Check whether the request reached WordPress. Cached or upstream traffic may be outside this observer.
A button or page is unavailable
Account, site/network context, permissions and active package pair.
Whether another administrator or tab changed the saved configuration.
Reload the current values, review your intended change and save again.
The live demo will not save or export
The demo banner and allowed actions.
This is intentional. Use a separate staging installation to test writes or downloads.
Note the exact message, time and timezone before changing settings. If you can reproduce the issue safely, use a fictional test record on staging rather than editing customer data.
A content or evidence link is missing
Check the selected site, current item/evidence permissions and retention. Deleted content and removed or expired evidence cannot be reopened. A current content title is only navigation context; it cannot restore a missing historical value. A synthetic alert test has no real triggering evidence. For Save this Activity view, remove unsupported free text and use a Recorded action filter. None of these checks requires broadening someone’s access.
Collection paused or report records unavailable
Read System status before trying to recreate data. Unreadable privacy settings require a deliberate valid settings save; busy privacy coordination can be retried. Inconsistent report metadata can leave an owner-visible job available for cancellation while output is refused. Neither repair recreates evidence that expired, was erased or was never collected.
Why one failed sign-in can leave no Activity row
Failed sign-ins are grouped: ten observed failures in the same fixed five-minute interval create a burst entry. Fewer failures have no individual Activity entries. Intervals restart every five minutes, so attempts on different sides of a boundary count separately. Supported WordPress failures against an existing account can also create a separate account-targeted burst. This identifies the account targeted, not the person attempting to sign in; passwords and attempted login text are not retained.
Requests contains matching findings, not a complete sign-in or traffic log. An upstream block or unsupported authentication integration may never reach the supported WordPress hooks. If an expected burst is missing, inspect System status and collection coverage.
Separate background work from delivery
Common work and delivery states
State or symptom
What it tells you
Useful action
Pending / queued
Work has been admitted, not necessarily completed.
Inspect that export, report or alert’s history and the host’s WordPress cron setup.
Suppressed / cancelled
A rule, permission or current configuration prevented this attempt.
Read the recorded reason. Do not assume that repeating the same request will deliver it.
Accepted by transport
The mail subsystem or destination transport accepted the attempt.
Check the recipient mailbox or receiving application and its delivery logs; acceptance does not prove receipt.
Delivery unknown
The outcome of an interrupted attempt could not be confirmed.
Check delivery history and the receiving system before attempting a manual resend.
Background export unavailable
Its private-storage or encryption requirements may be missing.
Read the interface’s prerequisite message. For a small activity selection, consider Download now instead.
For advanced alerts, inspect both the saved rule and its destination state. A successful background tick does not prove that every queued job completed. New saved exports use encrypted database chunks and require PHP Sodium, the original WordPress authentication salts and working scheduling. If an older job still uses private files, preserve its original storage and owner-only permissions for reads and cleanup; do not make a legacy export directory public to bypass an error.
Prepare a useful support record
Open Settings → System status and copy the exact finite error/state code, plus the time it occurred.
Under Diagnostic export preview, inspect the complete JSON before choosing Download diagnostic JSON.
The preview expires after five minutes. Reload for a fresh preview if it expires or your access changes.
Send the symptom, shortest safe reproduction, expected result, actual result and versions. Include the reviewed diagnostic file only when useful.
What the diagnostic JSON includes
Versions, scoped queue counts, configuration flags, sanitized state codes and permitted table-size estimates. It excludes audit records, account identifiers, email addresses, destination URLs, credentials and private paths. A diagnostic download is not an evidence export.
Keep the report focused
Do not paste licence keys, webhook URLs, encryption keys, raw activity or customer details into an ordinary support message. Use Support for the appropriate contact route.
Chapter 17 · Reference · Free & Pro
Update the pair and resume a schema upgrade
Update Free and Pro in order, confirm the result, and resume a paused database upgrade without losing its recorded progress.
Update Free first, then the compatible Pro ZIP. If a schema upgrade is pending, follow its saved phase; uninstalling is not a recovery method.
Prepare, update and verify
Keep a current backup of the database, plugin files and separately configured private keys/storage. Keep the previous compatible ZIPs available.
Test on staging. This guide covers Free 1.2.7 and Pro 1.2.7, requiring WordPress 6.7+ and PHP 8.0+ with the supported MySQL/MariaDB connection. Pro requires Free 1.2.7 or later with edition API 2. Check the download page for versions currently available.
Update Free first, then the matching Pro ZIP if you use Pro. Keep Free active. Do not uninstall to update.
Open Logged.ai and read any compatibility or schema message. If Schema upgrade is offered, inspect its status and choose Run next upgrade phase.
Continue from the recorded phase until complete. Each submission advances one resumable phase; scheduled work may also resume it when WordPress cron runs.
Check Settings → System status, saved configuration and one harmless representative workflow on staging. Confirm an expected new record, rather than relying on successful activation alone.
What “schema” means
The database structure the installed code expects. A plugin-file update and a database-structure update are related, but they are not the same operation.
Updating to 1.2.7: first confirm that the release is available from the download page and your account. Back up and test the compatible pair on staging. In WordPress, choose Plugins → Add New Plugin → Upload Plugin → Replace current with uploaded. Replace Free first, then Pro in a separate upload; keep Free active and do not uninstall either plugin. Free-only sites replace only Free. An update offer is separate from a successful installation and must pass the usual compatibility, entitlement and archive checks.
If the upgrade pauses
Read the message before acting
What you see
Meaning
Next step
Another schema upgrade is running
A lock protects an upgrade already in progress.
Wait and retry later; do not bypass or delete the lock.
A phase did not finish
The saved checkpoint identifies where work stopped.
Preserve the exact code and retry from Schema upgrade after resolving the reported cause.
Retry could not be scheduled
Automatic continuation was not scheduled.
Return to Schema upgrade and run the next phase manually with the required authority.
State unavailable or invalid
Progress cannot be safely read or verified.
Preserve the message and contact support. Do not reset checkpoints or delete tables.
While an incompatible phase is pending, capture and background work needing that schema may pause; compatible request policies can continue. Missed activity cannot be reconstructed later.
A code rollback is not a database restore
Replacing plugin files does not undo database changes. Recovery needs code compatible with the current data; coordinate any restore with the site owner and current customer activity.
Choose how to obtain the compatible packages
Free is available from Downloads (Release notes); Pro account downloads provide the compatible private package. Replacing compatible ZIPs preserves an existing local activation. A first-time Pro installation still needs licence activation to unlock new work.
When upgrading a Pro installation initialized before 0.1.8, local access is retained on its current canonical site and environment. It does not grant paid updates or reserve a licence slot. Moving the site, removing its saved connection, successfully completing the plugin’s Release licence slot action or uninstalling Pro can require activation again. Keep the previous pair and a current backup; replace files without uninstalling. Previously accepted purchase terms are not rewritten.
For the in-plugin route, follow Activate Pro and manage updates. It uses WordPress HTTPS and checks private temporary storage, PHP ZIP and WordPress file access before an update. An unavailable connection does not turn uninstalling into a safe update method.
These instructions describe Free 1.2.7 with Pro 1.2.7. Scoped checks do not certify every host or extension. Read the package notes and test representative workflows on staging before updating production.
After the one-time manual bridge
An offered Pro update must identify a compatible installed Free version. The private updater must also accept the compatibility profile, supported schema, commercial entitlement and offered archive. Check the available release and its package notes rather than assuming that documentation implies a live offer. Background automatic installation remains disabled; verify the result of an explicit update before retrying.
Update authority is checked before WordPress’s ordinary deactivation. A later installation failure can still leave Pro inactive even when WordPress restores its previous files. Read the error, confirm a compatible pair, then reactivate Pro from Plugins if instructed. No custom automatic reactivation is performed.
Quick reference
Plain-language glossary
Use these definitions when reading a finding, a case or a support message.
Actor
The recorded user or execution context that performed the observed operation. It may be a background task or be unknown.
Affected object / subject
The user, post, setting or other object affected. Example: when Alex changes Maya’s role, Alex is the actor and Maya is the affected account.
Outcome
The collector’s observed result, such as a recorded change, completed operation, attempt, failure or unknown result. An attempt is not proof of success.
Activity event
A supported WordPress or WooCommerce operation recorded by an activity collector. It describes an observed action and its context.
Request finding
A minimized request observation matching a local structural rule. It is a reason to review context, not proof of malicious intent or compromise.
Pattern
A documented structural match or bounded repeated-resource observation. Authorized scanners and ordinary diagnostics can also produce a pattern.
Case
A Pro investigation workspace that brings related retained evidence together with review status, notes and decisions. Its association or priority is not a verdict.
Retention
How long a category of evidence stays eligible to be kept before cleanup. Shortening it can permanently remove older evidence; increasing it does not restore deleted records.
Preview / Apply
A preview lets you inspect proposed results. Apply or Save commits the specific action after its required review and confirmation; a preview by itself does not do that.
Job
A queued unit of background work, such as preparing an export, generating a report or attempting a notification. Queued does not mean completed or delivered.
UTC
The time reference used for stored evidence and date-filter bounds. A screen can display a local timezone; read its label before comparing a displayed time with a UTC filter.
Correlation / association
A relationship between retained observations. Sharing a local request ID is stronger than sharing an address and time, but neither identifies one human or proves malicious intent or causality.