Choose your critical security and failure notices
Choose a small set of important events, authorize the right recipients, and verify the saved settings and delivery state.
For Free 1.2.7 and Pro 1.2.7. Check the download page for available versions and requirements. Verify representative workflows on staging before use.
Free and Pro notification boundaries
From 1.2.0, ordinary plugin-install notification emails require Pro. Administrator creation or promotion, unsafe registration changes, confirmed administrative email changes, selected security-component deactivation, failed-authentication bursts, admitted request findings and response-suppression/failure notices remain Free. These rules still require explicit configuration; no new messages are enabled automatically. Retained routine rules are paused without the activated add-on. Subscription expiry preserves earned local Pro use under the existing licence terms.
On this page
You will have an intentional alert configuration and know the difference between a queued notification, mail acceptance and actual receipt.
Logged.ai → Alerts → Fixed alerts
Critical security and failure notices are available in Free and Pro. Routine activity notification emails require the separately installed, activated Pro add-on. You need alert-management permission. Recipients must be WordPress accounts with current access to this site’s evidence and a valid account email address.
Start with a few events that require action. If you need custom thresholds, grouping or webhook destinations, use Pro advanced alerts.
- Under Choose what matters, select relevant fixed rules. Examples include administrator creation or promotion and a bounded failed-authentication burst in Free. Ordinary plugin-install emails require Pro.
- Under Choose who receives it, choose up to five eligible WordPress accounts. Selecting a recipient does not grant them evidence access.
- Set Cooldown in seconds from
60to86400. For example,3600means one hour of suppression for repeated matching alert work; it does not stop activity collection. - If using the selected security-component deactivation rule, choose the installed components you intend to watch. This is your classification of those components, not a guarantee of their protection.
- Choose Save alert settings. Reopen the page and confirm the selected rules, recipients and cooldown.
A failed-authentication burst requires ten observed failures in the same fixed five-minute interval. It is not a per-attempt notification. Read how failed sign-ins are grouped and what the collector can observe.
Fictional setup
A small site wants the responsible reviewer to know about administrator promotions in Free and, with Pro, new plugin installations. Select the available rules, choose that reviewer’s authorized WordPress account and set a one-hour cooldown. Verify receipt during an already-planned staging change; do not promote a production account merely to test an alert.
After a new matching event, inspect Recent delivery work. Alerts contain a short description and an authenticated evidence link. A queue entry is not delivery, and acceptance by WordPress mail is not proof that the message arrived in an inbox.
- Cooldown suppression: repeated matches can be intentionally suppressed.
- Changed configuration: new rules or recipients cancel older queued work; they do not replay old work to the new recipient.
- Delivery unknown: a crashed sending attempt is not silently repeated. Check the recipient and mail-system evidence before deciding what to do.
- Synthetic entries: explicitly labelled tests are tracked separately from ordinary matches.
Before sending, Logged.ai rechecks the current recipient, permission, consent and supporting evidence. A changed or revoked setting can stop a queued attempt. An interrupted attempt with an uncertain outcome is not automatically repeated; check the destination and diagnostics before sending another test.
Understand a failed or uncertain mail attempt
Free fixed alerts keep their existing maximum of three attempts when the WordPress mail call returns false, with retries after one and five minutes. If a server accepts the message but its acknowledgement is lost, a later retry can deliver a duplicate. An interrupted attempt is not blindly repeated. Mail-system acceptance is not proof of inbox delivery, and delivery is not exactly once.
- Confirm a relevant new event exists and matches an enabled rule.
- Check the recorded delivery state and the recipient’s current evidence access.
- Ask the intended recipient to confirm the message and open its authenticated link. Only that final check establishes receipt.
Nothing arrives
First separate “no matching evidence”, “no delivery work” and “mail accepted but not received”. Check rules, current recipients and cooldown, then System status and the site’s cron/mail setup as appropriate. Saving repeatedly is not a delivery test. See troubleshooting.
Free security notices and Pro activity emails
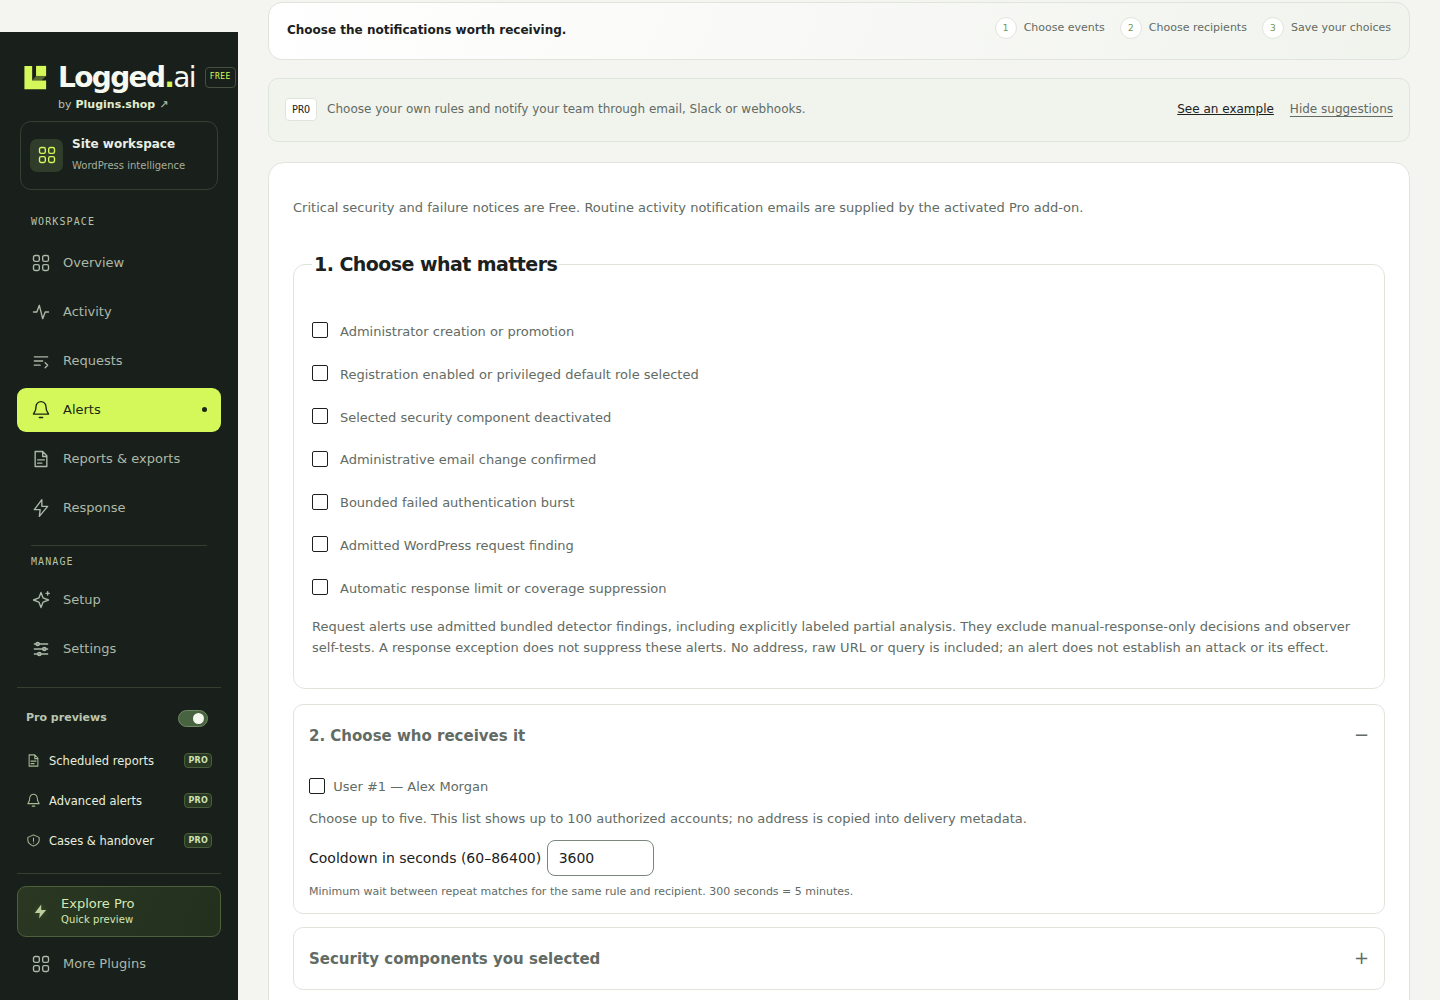
Choose critical security and failure notices and authorized recipients. All shown choices are disabled; this read-only demo sends no email.
Actual Logged.ai Free 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demo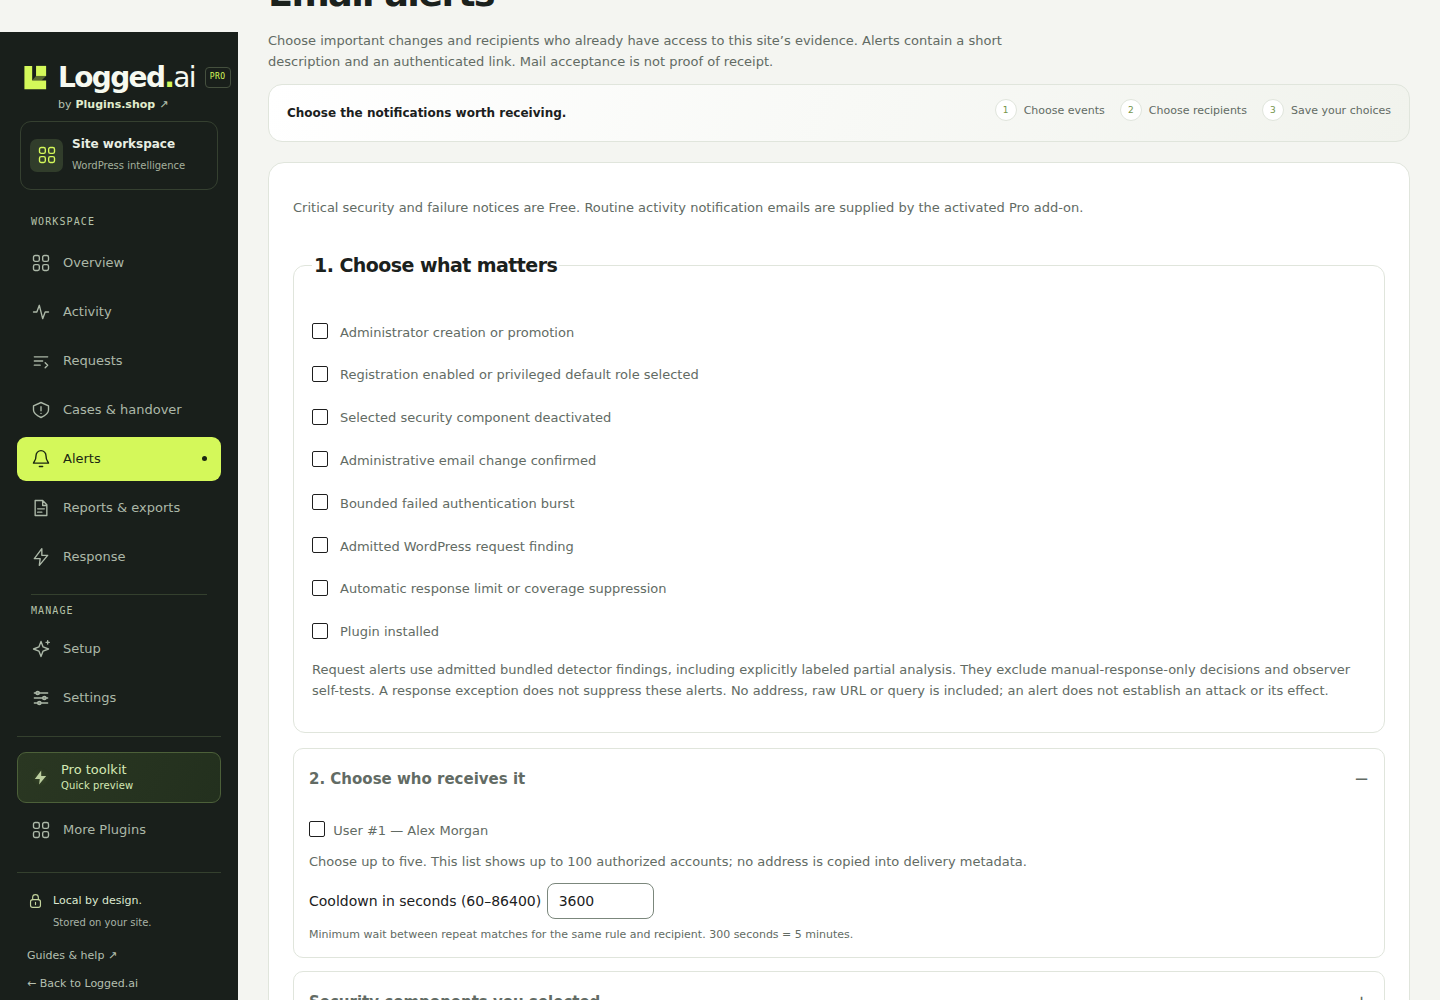
Activated Pro also provides ordinary plugin-install notices. The pictured fictional example has no enabled recipient or delivery.
Actual Logged.ai Pro 1.2.7, captured 9 November 2026 in the read-only demo. Fictional sample data dated 19 October 2026.Explore this screen in the demoThis guide covers Logged.ai Free 1.2.7 and Pro 1.2.7. Check available versions and package requirements, and verify representative workflows on staging before updating your main site.
Get help with your next step.